Outlook | Windows | Classic Outlook for Windows | For business
Using classic Outlook for Windows in business environments

This browser is no longer supported.
Upgrade to Microsoft Edge to take advantage of the latest features, security updates, and technical support.
' cx='32' cy='32' r='32' /%3E%3Ctext x='50%25' y='55%25' dominant-baseline='middle' text-anchor='middle' fill='%23FFF' %3EJR%3C/text%3E%3C/svg%3E)
Hi
The pictures below started popping up on our PCs. and the PC was using not part of any domain. I tried to follow the link below but the IE was inaccessible. https://answers.microsoft.com/en-us/outlook_com/forum/all/outlookoffice365com-security-certificate-has-been/743bdb2b-06ce-4206-923e-bdb7041528bd
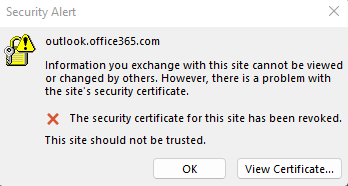
Using classic Outlook for Windows in business environments

I am not a computer person and also have this problem. I clicked into the Security Alert message's "View Certificate" button and saw that the certificate is issued to "outlook.com" while the security message said the internet address "outlook.office365.com" has security concern. That to me essentially is a Microsoft mess up by using Peter's credential to do business as Paul.
I think that I started to have this pop up issue around when the new certificate became effective, that was 7/25/2022.
As to some PCs/Macs don't have the issue maybe because they already have the correct security certificate installed on their computers. There is no setting in my hotmail setup for me to change in Outlook, so so far I am dealing with it by clicking ok on the box everyday.
' cx='32' cy='32' r='32' /%3E%3Ctext x='50%25' y='55%25' dominant-baseline='middle' text-anchor='middle' fill='%23FFF' %3EJ%3C/text%3E%3C/svg%3E)
Within Microsoft 365 Admin Center [https://admin.microsoft.com], go to Health > Service Health. If it’s unavailable in your tenant, open a case with Microsoft and reference that advisory number and have them add it to your tenant.
' cx='32' cy='32' r='32' /%3E%3Ctext x='50%25' y='55%25' dominant-baseline='middle' text-anchor='middle' fill='%23FFF' %3ERM%3C/text%3E%3C/svg%3E)
Hmm, that advisory doesn't show for me, I have sent in a report mentioning the advisory # and this forum.
The more info they have the better.
Finally - Microsoft has posted an advisory [EX455084] on this issue.

Where can I find this advisory posting?
' cx='32' cy='32' r='32' /%3E%3Ctext x='50%25' y='55%25' dominant-baseline='middle' text-anchor='middle' fill='%23FFF' %3ED5%3C/text%3E%3C/svg%3E)
I see it in our portal now as well. I also clicked the link in the service announcement to reflect that my client was having the issue.
' cx='32' cy='32' r='32' /%3E%3Ctext x='50%25' y='55%25' dominant-baseline='middle' text-anchor='middle' fill='%23FFF' %3EM%3C/text%3E%3C/svg%3E)
When I had the error this morning, I see the below in my CAPI2 log. It lead me to checking the issuing CAs to see if I trusted them and I noticed I didn't have either of the intermediate CAs for DigiCert Cloud Services CA-1. I think I've seen it issued by both the new and old intermediate CA... Always the same root CA, and I have yet to find any certs that are listed as expired in the crl.
The list of CAs MS apparently uses is here, and I should have them installed already? https://learn.microsoft.com/en-us/microsoft-365/compliance/encryption-office-365-certificate-chains?view=o365-worldwide
I'm trying the two for the DigiCert Cloud Services CA-1 and will see what happens. I realize this doesn't match up with any revoked cert error, but I figured it doesn't hurt to try. I also see it's lsass, but again, figured it can't hurt to try.
I also find it strange that the 4 instances we have had this morning, 3 of the times it was after the person was away from the PC for a bit, and once was when it came out of hibernation this AM.
<CertVerifyCertificateChainPolicy>
  <Policy type="CERT_CHAIN_POLICY_MICROSOFT_ROOT" constant="7" />
  <Certificate fileRef="F7DA87B0B58B2A2EEC386EC7A60AB14D5A60A499.cer" subjectName="outlook.com" />
  <CertificateChain chainRef="{3BD14261-79CD-4F1C-9F04-D87B6752C13D}" />
  <Flags value="20000" MICROSOFT_ROOT_CERT_CHAIN_POLICY_CHECK_APPLICATION_ROOT_FLAG="true" />
  <Status chainIndex="0" elementIndex="2" />
  <EventAuxInfo ProcessName="lsass.exe" />
  <CorrelationAuxInfo TaskId="{5E002671-EFDF-4383-808F-B28A1CF1B431}" SeqNumber="1" />
  <Result value="800B0109">A certificate chain processed, but terminated in a root certificate which is not trusted by the trust provider.</Result>
</CertVerifyCertificateChainPolicy>
' cx='32' cy='32' r='32' /%3E%3Ctext x='50%25' y='55%25' dominant-baseline='middle' text-anchor='middle' fill='%23FFF' %3EJM%3C/text%3E%3C/svg%3E)
We push the Intermediate Cert on our test machines, and we still get the errors.
' cx='32' cy='32' r='32' /%3E%3Ctext x='50%25' y='55%25' dominant-baseline='middle' text-anchor='middle' fill='%23FFF' %3EMC%3C/text%3E%3C/svg%3E)
Morning,
I am new to this forum but wanted everyone's opinion. I have a small number of users that are experiencing this issue. So, I check the serial number from the issued DigiCert cert and cross-referenced the data with the website "https://certificate.revocationcheck.com/outlook.com". I noticed the serial number is different from the website and the issue cert. I wonder if this could be the cause for some of my users.

' cx='32' cy='32' r='32' /%3E%3Ctext x='50%25' y='55%25' dominant-baseline='middle' text-anchor='middle' fill='%23FFF' %3EC%3C/text%3E%3C/svg%3E)
The CRL's for the cert don't actually have the fingerprint in there.
Depending on which geographical area you connect from you will get a different load balancer and likely a different cert.
For the cert: 0f12dc8955821d6d936bcf34e50f60c5
The CRL's are:
----------
[1]CRL Distribution Point
Distribution Point Name:
Full Name:
URL=http://crl3.digicert.com/DigiCertCloudServicesCA-1-g1.crl
[2]CRL Distribution Point
Distribution Point Name:
Full Name:
URL=http://crl4.digicert.com/DigiCertCloudServicesCA-1-g1.crl
Neither of those CRL's have the fingerprint listed.
Both URL's return the same CRL: bebff6803b4d8f357a1b95d585b7a95340217f3a
----------
All entries in the revoked list are 0xxxxxx and only one 0f which is 0f153da..... which doesn't match this cert. Which is weird that it's erroring. That's as far as I've looked into it.
' cx='32' cy='32' r='32' /%3E%3Ctext x='50%25' y='55%25' dominant-baseline='middle' text-anchor='middle' fill='%23FFF' %3E9%3C/text%3E%3C/svg%3E)
More info
ON, Canada
Thumbprint = f7da87b0b58b2a2eec386ec7a60ab14d5a60a499
Serial = 0f12dc8955821d6d936bcf34e50f60c5
CRL & OCSP report
https://certificate.revocationcheck.com/d841795beb73bb7c9e78a3713e3af6e1a506e86a00b95235a0e45304acc6b69f/outlook.com
Correct me if I'm wrong but the report states that it is not revoked.
CRL information does say "Revocation information is updated at least once every twelve months "
CERTUIL OUTPUT
C:\temp>certutil -verify -urlfetch testoulook.crt.cer
Issuer:
CN=DigiCert Cloud Services CA-1
O=DigiCert Inc
C=US
Name Hash(sha1): 48b6a9e21293b3c020b12ace4e73649a3c67dc9b
Name Hash(md5): 15b99a482264ff73f2a208ddbefd9e98
Subject:
CN=outlook.com
O=Microsoft Corporation
L=Redmond
S=Washington
C=US
Name Hash(sha1): 830674a4478dcff5ece46d1b71e1ebe193d47d67
Name Hash(md5): f32ab5d9094e4f0bed302ed125cc82cd
Cert Serial Number: 0f12dc8955821d6d936bcf34e50f60c5
dwFlags = CA_VERIFY_FLAGS_CONSOLE_TRACE (0x20000000)
dwFlags = CA_VERIFY_FLAGS_DUMP_CHAIN (0x40000000)
ChainFlags = CERT_CHAIN_REVOCATION_CHECK_CHAIN_EXCLUDE_ROOT (0x40000000)
HCCE_LOCAL_MACHINE
CERT_CHAIN_POLICY_BASE
--------
CERT_CHAIN_CONTEXT --------
ChainContext.dwInfoStatus = CERT_TRUST_HAS_PREFERRED_ISSUER (0x100)
ChainContext.dwRevocationFreshnessTime: 19 Hours, 8 Minutes, 53 Seconds
SimpleChain.dwInfoStatus = CERT_TRUST_HAS_PREFERRED_ISSUER (0x100)
SimpleChain.dwRevocationFreshnessTime: 19 Hours, 8 Minutes, 53 Seconds
CertContext[0][0]: dwInfoStatus=102 dwErrorStatus=0
Issuer: CN=DigiCert Cloud Services CA-1, O=DigiCert Inc, C=US
NotBefore: 7/25/2022 8:00 PM
NotAfter: 7/25/2023 7:59 PM
Subject: CN=outlook.com, O=Microsoft Corporation, L=Redmond, S=Washington, C=US
Serial: 0f12dc8955821d6d936bcf34e50f60c5
SubjectAltName: DNS Name=.clo.footprintdns.com, DNS Name=.hotmail.com, DNS Name=.internal.outlook.com, DNS Name=.live.com, DNS Name=.nrb.footprintdns.com, DNS Name=.office.com, DNS Name=.office365.com, DNS Name=.outlook.com, DNS Name=*.outlook.office365.com, DNS Name=attachment.outlook.live.net, DNS Name=attachment.outlook.office.net, DNS Name=attachment.outlook.officeppe.net, DNS Name=attachments.office.net, DNS Name=attachments-sdf.office.net, DNS Name=ccs.login.microsoftonline.com, DNS Name=ccs-sdf.login.microsoftonline.com, DNS Name=hotmail.com, DNS Name=mail.services.live.com, DNS Name=office365.com, DNS Name=outlook.com, DNS Name=outlook.office.com, DNS Name=substrate.office.com, DNS Name=substrate-sdf.office.com
Cert: f7da87b0b58b2a2eec386ec7a60ab14d5a60a499
Element.dwInfoStatus = CERT_TRUST_HAS_KEY_MATCH_ISSUER (0x2)
Element.dwInfoStatus = CERT_TRUST_HAS_PREFERRED_ISSUER (0x100)
---------------- Certificate AIA ----------------
Verified "Certificate (0)" Time: 0 81b68d6cd2f221f8f534e677523bb236bba1dc56
[0.0] http://cacerts.digicert.com/DigiCertCloudServicesCA-1.crt
---------------- Certificate CDP ----------------
Verified "Base CRL (0a52)" Time: 0 a0f47f61e4f0b841cf49dffb063c3dc82325119d
[0.0] http://crl3.digicert.com/DigiCertCloudServicesCA-1-g1.crl
Verified "Base CRL (0a52)" Time: 0 a0f47f61e4f0b841cf49dffb063c3dc82325119d
[1.0] http://crl4.digicert.com/DigiCertCloudServicesCA-1-g1.crl
---------------- Base CRL CDP ----------------
No URLs "None" Time: 0 (null)
---------------- Certificate OCSP ----------------
Verified "OCSP" Time: 0 266ca90d4cf7f2c17376696ecdd431ba9794d485
[0.0] http://ocspx.digicert.com
--------------------------------
CRL (null):
Issuer: CN=DigiCert Cloud Services CA-1, O=DigiCert Inc, C=US
ThisUpdate: 11/2/2022 12:15 AM
NextUpdate: 11/8/2022 11:30 PM
CRL: 8913134d940671fe8638e88bd349fd55f791724c
Issuance[0] = 2.23.140.1.2.2
Application[0] = 1.3.6.1.5.5.7.3.2 Client Authentication
Application[1] = 1.3.6.1.5.5.7.3.1 Server Authentication
CertContext[0][1]: dwInfoStatus=102 dwErrorStatus=0
Issuer: CN=DigiCert Global Root CA, OU=www.digicert.com, O=DigiCert Inc, C=US
NotBefore: 8/4/2015 8:00 AM
NotAfter: 8/4/2030 8:00 AM
Subject: CN=DigiCert Cloud Services CA-1, O=DigiCert Inc, C=US
Serial: 019ec1c6bd3f597bb20c3338e551d877
Cert: 81b68d6cd2f221f8f534e677523bb236bba1dc56
Element.dwInfoStatus = CERT_TRUST_HAS_KEY_MATCH_ISSUER (0x2)
Element.dwInfoStatus = CERT_TRUST_HAS_PREFERRED_ISSUER (0x100)
---------------- Certificate AIA ----------------
No URLs "None" Time: 0 (null)
---------------- Certificate CDP ----------------
Verified "Base CRL (0288)" Time: 0 b57e588e3371a7fee13eaa737aefdf4e126dcf51
[0.0] http://crl4.digicert.com/DigiCertGlobalRootCA.crl
Verified "Base CRL (0288)" Time: 0 b57e588e3371a7fee13eaa737aefdf4e126dcf51
[1.0] http://crl3.digicert.com/DigiCertGlobalRootCA.crl
---------------- Base CRL CDP ----------------
No URLs "None" Time: 0 (null)
---------------- Certificate OCSP ----------------
Verified "OCSP" Time: 0 80d02a82ed91c45c253ac7f02d0e860f7dad676e
[0.0] http://ocsp.digicert.com
--------------------------------
CRL (null):
Issuer: CN=DigiCert Global Root CA, OU=www.digicert.com, O=DigiCert Inc, C=US
ThisUpdate: 11/1/2022 3:10 PM
NextUpdate: 11/8/2022 3:10 PM
CRL: 29770badf567892431ebfbc24697ed9b9317281c
Application[0] = 1.3.6.1.5.5.7.3.2 Client Authentication
Application[1] = 1.3.6.1.5.5.7.3.3 Code Signing
Application[2] = 1.3.6.1.5.5.7.3.4 Secure Email
Application[3] = 1.3.6.1.5.5.7.3.1 Server Authentication
Application[4] = 1.3.6.1.5.5.7.3.8 Time Stamping
CertContext[0][2]: dwInfoStatus=10a dwErrorStatus=0
Issuer: CN=DigiCert Global Root CA, OU=www.digicert.com, O=DigiCert Inc, C=US
NotBefore: 11/9/2006 8:00 PM
NotAfter: 11/9/2031 8:00 PM
Subject: CN=DigiCert Global Root CA, OU=www.digicert.com, O=DigiCert Inc, C=US
Serial: 083be056904246b1a1756ac95991c74a
Cert: a8985d3a65e5e5c4b2d7d66d40c6dd2fb19c5436
Element.dwInfoStatus = CERT_TRUST_HAS_KEY_MATCH_ISSUER (0x2)
Element.dwInfoStatus = CERT_TRUST_IS_SELF_SIGNED (0x8)
Element.dwInfoStatus = CERT_TRUST_HAS_PREFERRED_ISSUER (0x100)
---------------- Certificate AIA ----------------
No URLs "None" Time: 0 (null)
---------------- Certificate CDP ----------------
No URLs "None" Time: 0 (null)
---------------- Certificate OCSP ----------------
No URLs "None" Time: 0 (null)
--------------------------------
Application[0] = 1.3.6.1.5.5.7.3.2 Client Authentication
Application[1] = 1.3.6.1.5.5.7.3.3 Code Signing
Application[2] = 1.3.6.1.5.5.7.3.4 Secure Email
Application[3] = 1.3.6.1.5.5.7.3.1 Server Authentication
Application[4] = 1.3.6.1.5.5.7.3.8 Time Stamping
EV[0] = 2.16.840.1.114412.2.1
EV[1] = 2.23.140.1.3
Exclude leaf cert:
Chain: a8f25e97a4ef94994351f1a0b09068320cd7f732
Full chain:
Chain: 72d2e243f0cc9ff042e9d321fd51a4fdb6c2d364
------------------------------------
Verified Issuance Policies:
2.23.140.1.2.2
Verified Application Policies:
1.3.6.1.5.5.7.3.2 Client Authentication
1.3.6.1.5.5.7.3.1 Server Authentication
Cert is an End Entity certificate
Leaf certificate revocation check passed
CertUtil: -verify command completed successfully.
So its is not revoked, but outlook is stating otherwise.
