Outlook | Windows | Classic Outlook for Windows | For business
Using classic Outlook for Windows in business environments

This browser is no longer supported.
Upgrade to Microsoft Edge to take advantage of the latest features, security updates, and technical support.
' cx='32' cy='32' r='32' /%3E%3Ctext x='50%25' y='55%25' dominant-baseline='middle' text-anchor='middle' fill='%23FFF' %3EJR%3C/text%3E%3C/svg%3E)
Hi
The pictures below started popping up on our PCs. and the PC was using not part of any domain. I tried to follow the link below but the IE was inaccessible. https://answers.microsoft.com/en-us/outlook_com/forum/all/outlookoffice365com-security-certificate-has-been/743bdb2b-06ce-4206-923e-bdb7041528bd
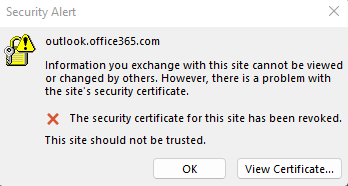
Using classic Outlook for Windows in business environments

I am not a computer person and also have this problem. I clicked into the Security Alert message's "View Certificate" button and saw that the certificate is issued to "outlook.com" while the security message said the internet address "outlook.office365.com" has security concern. That to me essentially is a Microsoft mess up by using Peter's credential to do business as Paul.
I think that I started to have this pop up issue around when the new certificate became effective, that was 7/25/2022.
As to some PCs/Macs don't have the issue maybe because they already have the correct security certificate installed on their computers. There is no setting in my hotmail setup for me to change in Outlook, so so far I am dealing with it by clicking ok on the box everyday.
' cx='32' cy='32' r='32' /%3E%3Ctext x='50%25' y='55%25' dominant-baseline='middle' text-anchor='middle' fill='%23FFF' %3EJC%3C/text%3E%3C/svg%3E)
INFORMATION UPDATE:
My coworker just got off the phone with Microsoft Support and we were told that this is a Global Issue, and that they are working to resolve it.
For a reference I have left the case number below if you happen to call-in/chat with support.
CASE# 33672891
' cx='32' cy='32' r='32' /%3E%3Ctext x='50%25' y='55%25' dominant-baseline='middle' text-anchor='middle' fill='%23FFF' %3EC%3C/text%3E%3C/svg%3E)
Case # 33676192 Here..
Keep calling them in and reference the two other cases if you can. It seems to be all Canada East area / regional issues
' cx='32' cy='32' r='32' /%3E%3Ctext x='50%25' y='55%25' dominant-baseline='middle' text-anchor='middle' fill='%23FFF' %3ECR%3C/text%3E%3C/svg%3E)
It's not just Canada area. I've stated I live in KY (USA) and several of my customers are experiencing this issue.
' cx='32' cy='32' r='32' /%3E%3Ctext x='50%25' y='55%25' dominant-baseline='middle' text-anchor='middle' fill='%23FFF' %3ED5%3C/text%3E%3C/svg%3E)
My case is #:33659688 They are asking me to do a remote connectivity analyzer test, which I believe succeeded 100% if I recall the previous 20 times, I ran it this week doing my troubleshooting.
' cx='32' cy='32' r='32' /%3E%3Ctext x='50%25' y='55%25' dominant-baseline='middle' text-anchor='middle' fill='%23FFF' %3ECR%3C/text%3E%3C/svg%3E)
Believe me, I understand how frustrating an intermittent issue is to troubleshoot, but Microsoft needs to understand that this often can't be replicated. If you haven't already, I'd suggest pointing them to this thread to see how broadly it's impacting people by geographic location, datacentre, tenant, connection, on-prem/off-prem, OS, and Outlook client. Perhaps even point them to the other case mentioned in this thread 33672891.
Seems like they're finally aware at least.
Not that those dealing with this issue want to hear this, but we haven't had any reported reoccurrences since last Friday (October 28th).
Chris
I provided the thread in my ticket response to them already and sited that others have cases open and that this is not isolated to my client
Hello neighbor, we are located in Brownsville, Tennessee.
' cx='32' cy='32' r='32' /%3E%3Ctext x='50%25' y='55%25' dominant-baseline='middle' text-anchor='middle' fill='%23FFF' %3EM%3C/text%3E%3C/svg%3E)
When I had the error this morning, I see the below in my CAPI2 log. It lead me to checking the issuing CAs to see if I trusted them and I noticed I didn't have either of the intermediate CAs for DigiCert Cloud Services CA-1. I think I've seen it issued by both the new and old intermediate CA... Always the same root CA, and I have yet to find any certs that are listed as expired in the crl.
The list of CAs MS apparently uses is here, and I should have them installed already? https://learn.microsoft.com/en-us/microsoft-365/compliance/encryption-office-365-certificate-chains?view=o365-worldwide
I'm trying the two for the DigiCert Cloud Services CA-1 and will see what happens. I realize this doesn't match up with any revoked cert error, but I figured it doesn't hurt to try. I also see it's lsass, but again, figured it can't hurt to try.
I also find it strange that the 4 instances we have had this morning, 3 of the times it was after the person was away from the PC for a bit, and once was when it came out of hibernation this AM.
<CertVerifyCertificateChainPolicy>
  <Policy type="CERT_CHAIN_POLICY_MICROSOFT_ROOT" constant="7" />
  <Certificate fileRef="F7DA87B0B58B2A2EEC386EC7A60AB14D5A60A499.cer" subjectName="outlook.com" />
  <CertificateChain chainRef="{3BD14261-79CD-4F1C-9F04-D87B6752C13D}" />
  <Flags value="20000" MICROSOFT_ROOT_CERT_CHAIN_POLICY_CHECK_APPLICATION_ROOT_FLAG="true" />
  <Status chainIndex="0" elementIndex="2" />
  <EventAuxInfo ProcessName="lsass.exe" />
  <CorrelationAuxInfo TaskId="{5E002671-EFDF-4383-808F-B28A1CF1B431}" SeqNumber="1" />
  <Result value="800B0109">A certificate chain processed, but terminated in a root certificate which is not trusted by the trust provider.</Result>
</CertVerifyCertificateChainPolicy>
' cx='32' cy='32' r='32' /%3E%3Ctext x='50%25' y='55%25' dominant-baseline='middle' text-anchor='middle' fill='%23FFF' %3EJM%3C/text%3E%3C/svg%3E)
We push the Intermediate Cert on our test machines, and we still get the errors.
' cx='32' cy='32' r='32' /%3E%3Ctext x='50%25' y='55%25' dominant-baseline='middle' text-anchor='middle' fill='%23FFF' %3EJ%3C/text%3E%3C/svg%3E)
Finally - Microsoft has posted an advisory [EX455084] on this issue.

' cx='32' cy='32' r='32' /%3E%3Ctext x='50%25' y='55%25' dominant-baseline='middle' text-anchor='middle' fill='%23FFF' %3ERM%3C/text%3E%3C/svg%3E)
Where can I find this advisory posting?
I see it in our portal now as well. I also clicked the link in the service announcement to reflect that my client was having the issue.
Within Microsoft 365 Admin Center [https://admin.microsoft.com], go to Health > Service Health. If it’s unavailable in your tenant, open a case with Microsoft and reference that advisory number and have them add it to your tenant.
Hmm, that advisory doesn't show for me, I have sent in a report mentioning the advisory # and this forum.
The more info they have the better.
' cx='32' cy='32' r='32' /%3E%3Ctext x='50%25' y='55%25' dominant-baseline='middle' text-anchor='middle' fill='%23FFF' %3EAL%3C/text%3E%3C/svg%3E)
What it looks like to me is they revoked a SSL they were using globally across their 1000s of Exchange server farm. When they revoked the original SSL they have updated most of the servers w the new generated certificate and have overlooked a server or two. Hence why it’s intermittent and only happening to random users.
If they had just one server and the ssl was revoked everyone would get the same error all the time.
Yes, that is exactly what has happened, but all we can do is keep reporting where we see it and hope that helps MS narrow down which server(s) have the old cert.
Ideally MS should be able to whip together a Powershell script to check the certs on their servers and let them know which ones are non-compliant. This shouldn't have to happen.
