Outlook | Windows | Classic Outlook for Windows | For business
Using classic Outlook for Windows in business environments

This browser is no longer supported.
Upgrade to Microsoft Edge to take advantage of the latest features, security updates, and technical support.
' cx='32' cy='32' r='32' /%3E%3Ctext x='50%25' y='55%25' dominant-baseline='middle' text-anchor='middle' fill='%23FFF' %3EJR%3C/text%3E%3C/svg%3E)
Hi
The pictures below started popping up on our PCs. and the PC was using not part of any domain. I tried to follow the link below but the IE was inaccessible. https://answers.microsoft.com/en-us/outlook_com/forum/all/outlookoffice365com-security-certificate-has-been/743bdb2b-06ce-4206-923e-bdb7041528bd
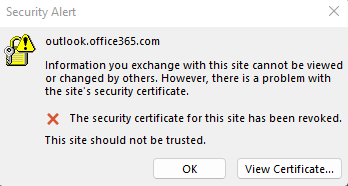
Using classic Outlook for Windows in business environments

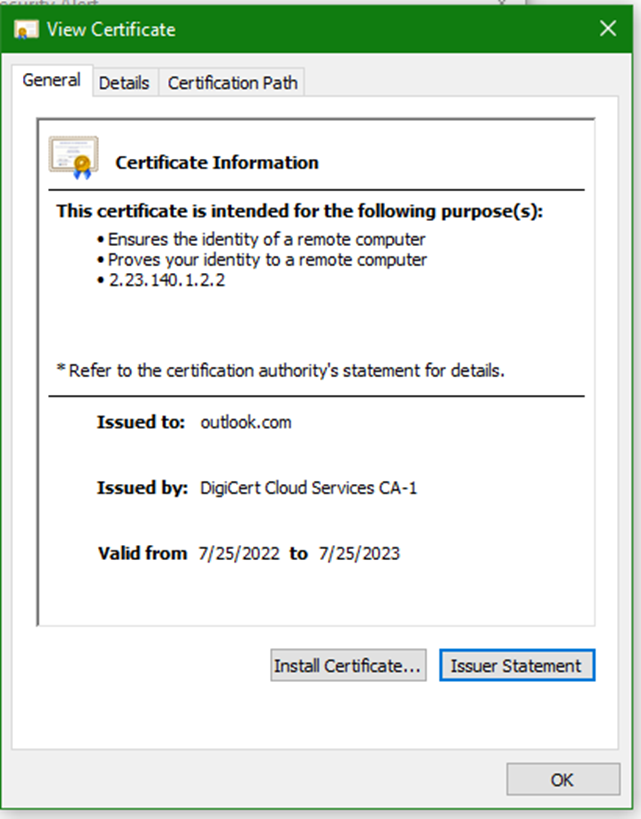
I am not a computer person and also have this problem. I clicked into the Security Alert message's "View Certificate" button and saw that the certificate is issued to "outlook.com" while the security message said the internet address "outlook.office365.com" has security concern. That to me essentially is a Microsoft mess up by using Peter's credential to do business as Paul.
I think that I started to have this pop up issue around when the new certificate became effective, that was 7/25/2022.
As to some PCs/Macs don't have the issue maybe because they already have the correct security certificate installed on their computers. There is no setting in my hotmail setup for me to change in Outlook, so so far I am dealing with it by clicking ok on the box everyday.
' cx='32' cy='32' r='32' /%3E%3Ctext x='50%25' y='55%25' dominant-baseline='middle' text-anchor='middle' fill='%23FFF' %3EW%3C/text%3E%3C/svg%3E)
Any solutions from MS?
Same thing happens in our tenant, already created a case on MS support, no answer from the case owner so far.
' cx='32' cy='32' r='32' /%3E%3Ctext x='50%25' y='55%25' dominant-baseline='middle' text-anchor='middle' fill='%23FFF' %3ET%3C/text%3E%3C/svg%3E)
According to MS this is fixed now, but better just monitor and see
Final status: Our analysis of the Outlook client diagnostic and memory process logs identified a subset of network infrastructure that processes Transport Layer Security (TLS) requests wasn't functioning as expect, resulting in impact. We've disabled this problematic network path, allowing traffic to flow through alternate routes and remediating impact.
Root cause: A subset of network infrastructure that processes TLS requests wasn't functioning as expect, resulting in impact.
Next steps:
This is the final update for the event.
' cx='32' cy='32' r='32' /%3E%3Ctext x='50%25' y='55%25' dominant-baseline='middle' text-anchor='middle' fill='%23FFF' %3ED%3C/text%3E%3C/svg%3E)
Thank you, Tim, for pursuing this with Microsoft, and sharing the answer from Microsoft as to the solution!
' cx='32' cy='32' r='32' /%3E%3Ctext x='50%25' y='55%25' dominant-baseline='middle' text-anchor='middle' fill='%23FFF' %3ESS%3C/text%3E%3C/svg%3E)
Also been seeing this for a few months now. My perception is it's happening to everyone and not many are complaining because they can click on OK and carry on. Happens at the office, at peoples homes, on windows 7, 10 and 11... and on iPhones too. Microsoft forgetting to update some servers makes the most sense to me.
' cx='32' cy='32' r='32' /%3E%3Ctext x='50%25' y='55%25' dominant-baseline='middle' text-anchor='middle' fill='%23FFF' %3EAD%3C/text%3E%3C/svg%3E)
Goodness, I see this has been an issue for many others as well. I'm in a hybrid AD and O365 environment with about 135 Windows 10 laptops. And I have ONE person that this is happening to when she's on the wired network at the office, as well as when she's at her home office. I'm about to open a support ticket with MS Support, but this needs to be fixed!
' cx='32' cy='32' r='32' /%3E%3Ctext x='50%25' y='55%25' dominant-baseline='middle' text-anchor='middle' fill='%23FFF' %3EJJ%3C/text%3E%3C/svg%3E)
We've been getting this as well. When we set up our Exchange DNS records for our corp, Microsoft instructs to CNAME your domain to autodiscover.outlook.com for auto discovery as per the CNAME records from the admin centre domain setup wizard. Curiously, autodiscover.outlook.com digs out to other cnames that apparently don't match "outlook.com" See below
C:\Users\jeffj>dig autodiscover.outlook.com
; <<>> DiG 9.16.28 <<>> autodiscover.outlook.com
;; global options: +cmd
;; Got answer:
;; ->>HEADER<<- opcode: QUERY, status: NOERROR, id: 36725
;; flags: qr rd ra; QUERY: 1, ANSWER: 6, AUTHORITY: 0, ADDITIONAL: 1
;; OPT PSEUDOSECTION:
; EDNS: version: 0, flags:; udp: 512
;; QUESTION SECTION:
;autodiscover.outlook.com. IN A
;; ANSWER SECTION:
autodiscover.outlook.com. 249 IN CNAME autod.ha-autod.office.com.
autod.ha-autod.office.com. 58 IN CNAME autod.ms-acdc-autod.office.com.
autod.ms-acdc-autod.office.com. 8 IN A 52.96.230.40
autod.ms-acdc-autod.office.com. 8 IN A 40.100.163.184
autod.ms-acdc-autod.office.com. 8 IN A 40.100.162.184
autod.ms-acdc-autod.office.com. 8 IN A 52.96.163.232
Microsoft's connectivity test uses autodiscover-s.outlook.com which of course always passes. Digging that shows that it cname's to outlook.office365.com
C:\Users\jeffj>dig autodiscover-s.outlook.com
; <<>> DiG 9.16.28 <<>> autodiscover-s.outlook.com
;; global options: +cmd
;; Got answer:
;; ->>HEADER<<- opcode: QUERY, status: NOERROR, id: 50587
;; flags: qr rd ra; QUERY: 1, ANSWER: 8, AUTHORITY: 0, ADDITIONAL: 1
;; OPT PSEUDOSECTION:
; EDNS: version: 0, flags:; udp: 512
;; QUESTION SECTION:
;autodiscover-s.outlook.com. IN A
;; ANSWER SECTION:
autodiscover-s.outlook.com. 130 IN CNAME outlook.office365.com.
outlook.office365.com. 151 IN CNAME outlook.ha.office365.com.
outlook.ha.office365.com. 54 IN CNAME outlook.ms-acdc.office.com.
outlook.ms-acdc.office.com. 3594 IN CNAME yyz-efz.ms-acdc.office.com.
yyz-efz.ms-acdc.office.com. 4 IN A 52.96.215.82
yyz-efz.ms-acdc.office.com. 4 IN A 52.96.88.226
yyz-efz.ms-acdc.office.com. 4 IN A 52.96.88.210
yyz-efz.ms-acdc.office.com. 4 IN A 52.96.230.226
I went ahead and changed my autodiscovery record in my corps dns to CNAME to autodiscover-s.outlook.com instead of the suggested autodiscover-s.outlook.com by Exchanges wizard and so far I have not had the Cert revoked error come back up.
Don't know if this s the definitive solution, but the workaround appears to work.
' cx='32' cy='32' r='32' /%3E%3Ctext x='50%25' y='55%25' dominant-baseline='middle' text-anchor='middle' fill='%23FFF' %3EAL%3C/text%3E%3C/svg%3E)
What it looks like to me is they revoked a SSL they were using globally across their 1000s of Exchange server farm. When they revoked the original SSL they have updated most of the servers w the new generated certificate and have overlooked a server or two. Hence why it’s intermittent and only happening to random users.
If they had just one server and the ssl was revoked everyone would get the same error all the time.
' cx='32' cy='32' r='32' /%3E%3Ctext x='50%25' y='55%25' dominant-baseline='middle' text-anchor='middle' fill='%23FFF' %3ERM%3C/text%3E%3C/svg%3E)
Yes, that is exactly what has happened, but all we can do is keep reporting where we see it and hope that helps MS narrow down which server(s) have the old cert.
Ideally MS should be able to whip together a Powershell script to check the certs on their servers and let them know which ones are non-compliant. This shouldn't have to happen.
