The Local Security Authority protection is off - Windows 11 Home

Anonymous
2023-03-17T06:10:20+00:00

A yellow triangle appeared on the Windows Security iron yesterday. It says that Local Security Authority protection is off. Your device may be vulnerable.

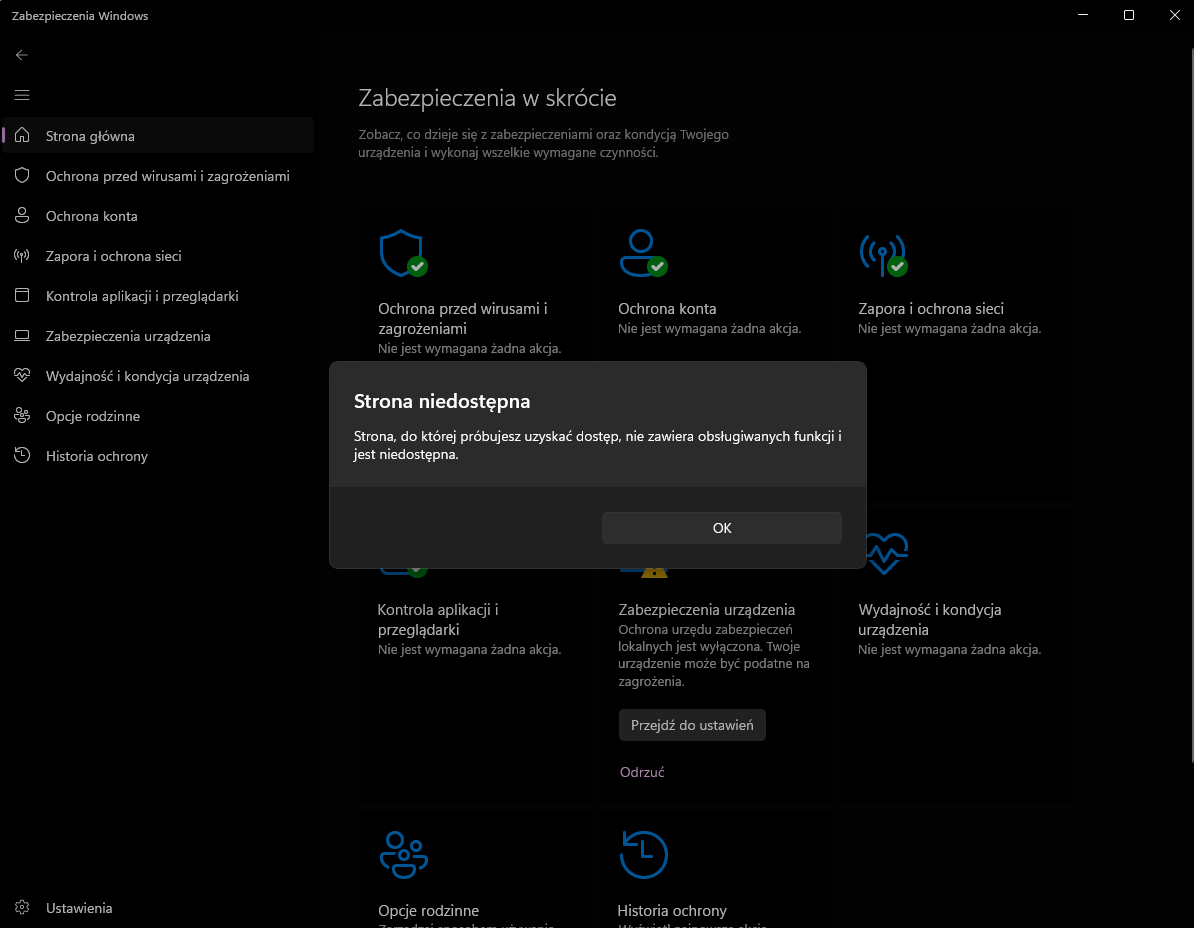
I can press Go to settings or Dismiss but when I click go to settings, a notification saying "the page You want to access doesn't contain required functions and is unavailable". 

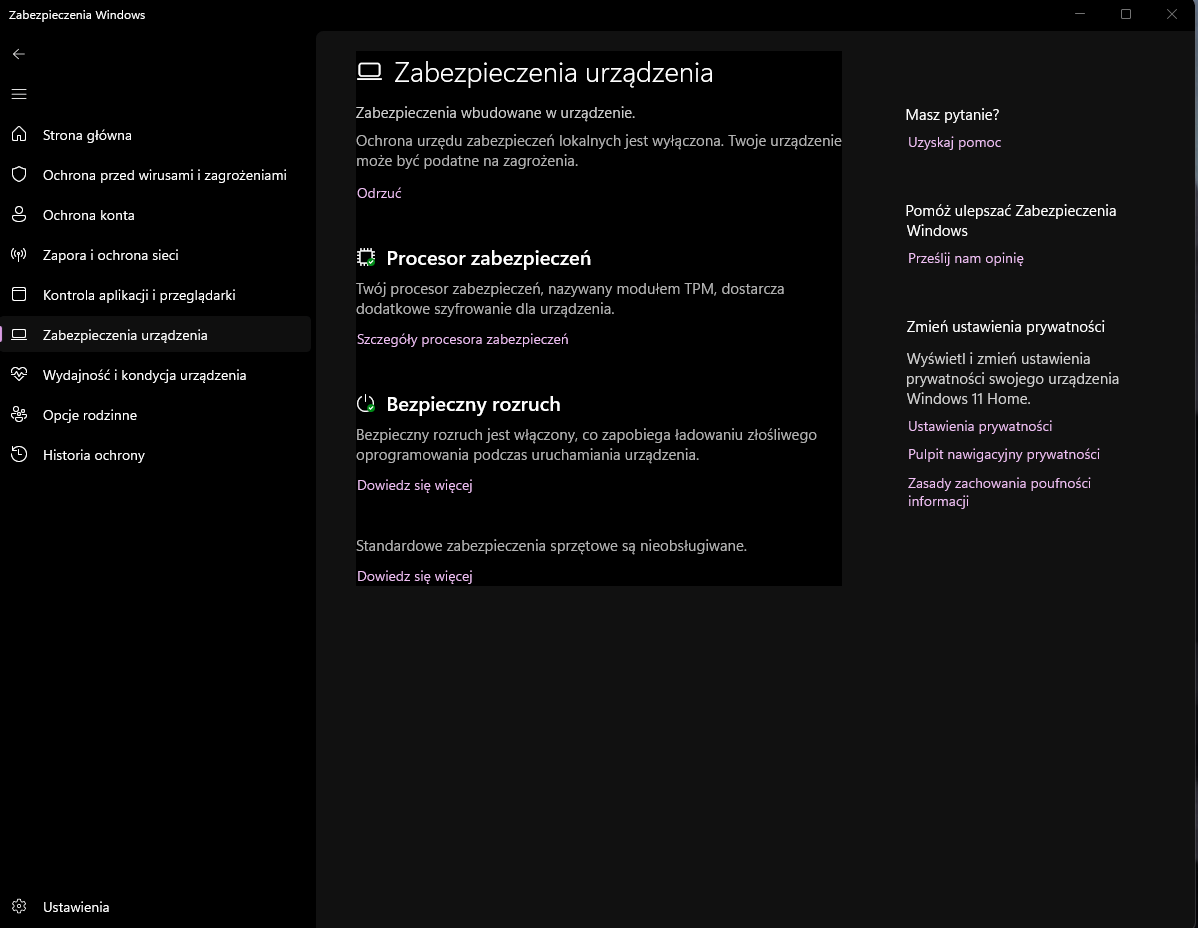
There is also no option to turn the protection on in the Device Security panel (there is only "dismiss" option).

When I was looking at it yesterday, there was also a notification that "The tpm module is unavailable" but today it doesn't show. I checked the device manager and uefi and both say that the tpm is enabled.

I've found an advice to turn on SMV in UEFI (in the CPU settings) to solve the problem but I don't want to change anything in BIOS without consultation as I'm no expert. I've also found a reply from a truste source that this whole problem is a Microsoft bug and it's better to just wait till they fix it.

What should I do?

Screenshots are in Polish, I hope they can be useful somehow. The first one shows the notification about a page being not available and the second shows the Device security panel (the notification from the first screenshot displays when I close the device security page or when I click on "go to settings" below the information that the protection is turned off). There is also an information (second screenshot) that "standard device security is not supported".
Windows for home | Windows 11 | Security and privacy

Locked Question. This question was migrated from the Microsoft Support Community. You can vote on whether it's helpful, but you can't add comments or replies or follow the question.

0 comments No comments
Answer accepted by question author
Anonymous
2023-07-06T07:36:56+00:00

Microsoft have just posted that they have resolved the "Local Security Authority protection is off" issue in an update. Has anyone tried to apply it from Windows Update?

Resolution: This issue was resolved in an update for Windows Security platform antimalware platform KB5007651 (Version 1.0.2306.10002). If you would like to install the update before it is installed automatically, you will need to check for updates.

Was this answer helpful?

10+ people found this answer helpful.
0 comments No comments

174 additional answers

Sort by: Most helpful
  1. Anonymous
    2023-05-24T11:23:58+00:00

    indeed nobody is sure that these manipulations in the register are without negative impact. And if we delete these 2 runasppl and runaspplboot entries, are we sure to return to the situation before these manipulations? Does anyone know more about deleting these 2 32-bit Word entries and therefore neutralizing or not their impact on the system? thanks for the feedback.

    Given the number of people who have followed this advice to create these 2 32-bit Word entries in the registry ( runasppl and runaspplboot ), yet highlighted on very specialized IT advice sites (and seen all the contradictory opinions 😡 ), it would be really interesting to know if a safe rollback is possible: sound advice on this welcome, it would help a lot of people 🙏

    Was this answer helpful?

    0 comments No comments
  2. Anonymous
    2023-05-24T08:22:33+00:00

    Hi, in their documentation Microsoft only recommends creating the runasppl entry if the lsa protection is missing and never mentions creating runaspplboot. When you read all the posts whether here or on other sites, it is generally recommended to create these 2 values ​​of Word 32 bits by giving them most of the time a value of 2 and sometimes a value of 1 but we do not really know what it is for: we just see that it turns off the Windows Security alert. As I read among other things that it was easier to undo the value of Word 32 bits 2 than the value 1, I always put 2 for this value (and indeed when we migrated to w11 22h2 , we must choose 2 for this value).
    Microsoft's link to this is here: https://learn.microsoft.com/fr-fr/windows-server/security/credentials-protection-and-management/configuring-additional-lsa-protection

    Was this answer helpful?

    0 comments No comments
  3. Anonymous
    2023-05-24T07:54:30+00:00

    Hi, in their documentation Microsoft only recommends creating the runasppl entry if the lsa protection is missing and never mentions creating runaspplboot. When you read all the posts whether here or on other sites, it is generally recommended to create these 2 values ​​of Word 32 bits by giving them most of the time a value of 2 and sometimes a value of 1 but we do not really know what it is for: we just see that it turns off the Windows Security alert. As I read among other things that it was easier to undo the value of Word 32 bits 2 than the value 1, I always put 2 for this value (and indeed when we migrated to w11 22h2 , we must choose 2 for this value).
    Microsoft's link to this is here: https://learn.microsoft.com/fr-fr/windows-server/security/credentials-protection-and-management/configuring-additional-lsa-protection

    Was this answer helpful?

    0 comments No comments
  4. Anonymous
    2023-05-24T01:55:36+00:00

    gerard so giving it a value of 1 would mean UEFI variable is enabled? here is where it is confusing if this is windows 11 updated from 10 or just installed new, is this UEFI variable 1 needed? I asked because of this information. UEFI for Windows 11: What You Need to Know (onlogic.com) any information would be great, I have had success using 2 instead of 1 I never tried 1 and after a restart and reset of setting to 0 then restart and change back to 2 everything works as needed. I was just wondering if you had more information about it?

    Was this answer helpful?

    0 comments No comments