I encounter this challenge in different setups since years. I solved it in the past, but didn't made notes on solution - so again read a lot of guessing, see that, try that...
Our Setup and Requirements
Clients: Windows 10 Pro, instructions also apply to Windows 10
NAS: Linux with Samba Shares, local users, Workgroup and NetBios.
Guest or anonymous access is disabled.
Workgroup = SAMEPCNASROUTER
Shares = //MAXIMUM-15-CHAR/*shared folder names*
A. Use Office 365 accounts
Devices joined Azure AD (no MDM).
Too small use case to integrate NAS with Azure AD, in effort and it requires additional Azure licenses on top of Office 365 Business plan. Therefore each user connects to NAS with their existing LAN user and pw.
Problem: Can't see or access Shares with these users, using NAS user
connect as
Login to NAS using local accounts with same WORKGROUP/ID/PW on NAS worked from scratch. See further treading how to test this yourself.
B. Drop SMB 1 and Update SMB Server on NAS
Windows SMB Client uses 3.11,
https://docs.microsoft.com/en-us/windows-server/storage/file-server/file-server-smb-overview
Problem: This NAS serves us since 10 years, and no firmware update includes SMB 3.
Check SMB version, here output after upgrade of SMB .
[insaneuser@maximum-15-char ~]#smb2status
smbd (samba daemon) Version 4.0.25
smbd (samba daemon) is running.
max protocol SMB 3 enabled.
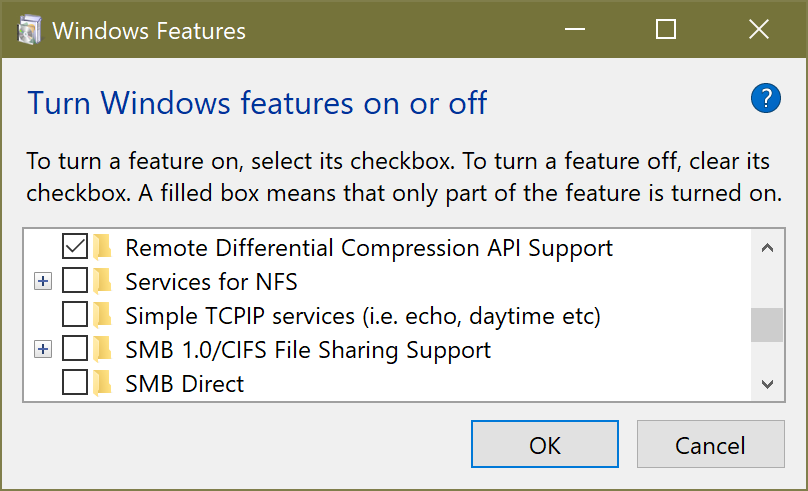
Turn off Windows Features 'SMB 1.0/CIFS File Sharing Support'. SMB DIrect' and 'NFS Client' (unchecked).
- Win + S >Turn Windows features on or off
C. Display NAS Host under Networks
NAS Host under Networks on Navigation pane of Windows Explorer must be shown.
Solution
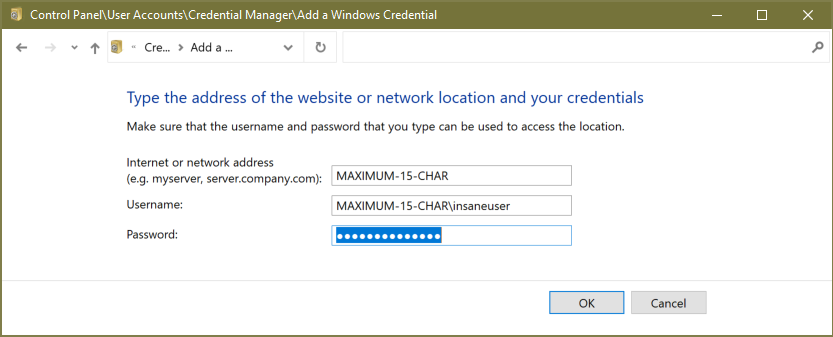
A. Windows Credential with NAS hostname
Use Windows Credential with NAS hostname instead of a domain.
- Win + S >Windows Credentials
- Add a Windows credential
- Set NAS host in front of username
maximum-15-char\insaneuser
B. Enable SMB 3 on NAS
Recommended SMB Configuration:
[insaneuser@maximum-15-char ~]#vi /etc/config/smb.conf
[global]
workgroup = SAMEPCNASROUTER
netbios = MAXIMUM-15-CHAR
min protocol = SMB2_02
max protocol = SMB3_11
SMB3 Settings of QNAP and Synology :
https://www.synology.com/en-global/knowledgebase/DSM/help/DSM/AdminCenter/file_winmacnfs_win
https://www.qnap.com/en/how-to/tutorial/article/how-to-use-smb-3-0-in-qts-4-2
C. Open a Share
It is not enough to map a network drive to see host and share under Navigation Networks.
You must first open a share, manually or by script.
We created a link to a share to each user home and pinned this link to Windows Explorer navigation pane.
Check and Set these Windows Configurations
RequireSecuritySignature
Windows is unable to access SMB shares on a NAS when SMB signing is enabled - In setup above this is off - 0
https://www.qnap.com/en/how-to/faq/article/windows-is-unable-to-access-smb-shares-on-a-nas-when-smb-signing-is-enabled-requiresecuritysignature1-how-can-i-fix-this-problem/
https://docs.netapp.com/ontap-9/index.jsp?topic=%2Fcom.netapp.doc.cdot-famg-cifs%2FGUID-EE6C5170-7CF6-492C-83A6-9904AE247F21.html
AllowInsecureGuestAuth
Windows is unable to see shares of hosts or show fallback. if is guest authentication is disabled - In setup above this is off - 0
https://docs.microsoft.com/en-us/troubleshoot/windows-server/networking/guest-access-in-smb2-is-disabled-by-default
Further Reading
Naming Windows Workgroups and Domains
https://www.lifewire.com/naming-windows-workgroups-818240
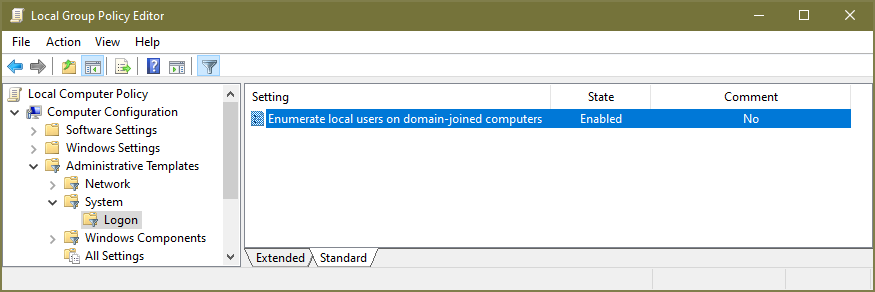
Enable Local Account Login on a Client joined Azure AD
In order to create a local test user account, this must be first enabled.
This is not needed for final solution:
- Win + S > Edit group policy
- enable Enumerate local users on domain-joined computers
HKLM\Software\Policies\Microsoft\Windows\System!EnumerateLocalUsers
3. after testing disable this setting. If you want to keep local accounts, read security considerations of Local
Accounts (MS Docs > Windows > Security Identity and access protection).
Tested Environment
QNAP T-259 Pro+, QTS 4.2.6 (20200611), samba daemon) Version 4.0.25
Microsoft Windows 10 Pro 10.0.19041 Build 19041
' cx='32' cy='32' r='32' /%3E%3Ctext x='50%25' y='55%25' dominant-baseline='middle' text-anchor='middle' fill='%23FFF' %3EA%3C/text%3E%3C/svg%3E)

' cx='32' cy='32' r='32' /%3E%3Ctext x='50%25' y='55%25' dominant-baseline='middle' text-anchor='middle' fill='%23FFF' %3EM%3C/text%3E%3C/svg%3E)