Exchange Online
A cloud-based service included in Microsoft 365, delivering scalable messaging and collaboration features with simplified management and automatic updates.
This browser is no longer supported.
Upgrade to Microsoft Edge to take advantage of the latest features, security updates, and technical support.
' cx='32' cy='32' r='32' /%3E%3Ctext x='50%25' y='55%25' dominant-baseline='middle' text-anchor='middle' fill='%23FFF' %3EDP%3C/text%3E%3C/svg%3E)
Hello everyone,
Our clients reported that one of the links in an email we're sending is being marked as malicious by Microsoft Defender. I've done a lot of searching and it seems like all the solution are tailored for the system administrators controlling a particular Microsoft Exchange / Microsoft office 365 instance and there is zero information about ways to appeal for cases like ours where our clients have a problem and not we.
One of the options frequently recommended is a submission portal - https://www.microsoft.com/en-us/wdsi/filesubmission/
However it clearly does not fit the case, because it's not about email attachment, the problem is about domain being marked as problematic.
What's the best way to solve this issue?
We've tried asking our clients to report false positives, tried raising paid support tickets, nothing helps
A cloud-based service included in Microsoft 365, delivering scalable messaging and collaboration features with simplified management and automatic updates.
Locked Question. You can vote on whether it's helpful, but you can't add comments or replies or follow the question.
' cx='32' cy='32' r='32' /%3E%3Ctext x='50%25' y='55%25' dominant-baseline='middle' text-anchor='middle' fill='%23FFF' %3EAL%3C/text%3E%3C/svg%3E)
Hi,
I am currently doing some research on this issue and will inform you as soon as possible.
Please be patient for a while…
Hi @Dmitry Petrov ,
It has been a few days and I am checking in to see how things are going on with this issue.
If it has been resolved, please click "Accept as answer" to mark useful post or share your solution, your action would benefit others who have similar issues. If you have any questions or need further assistance, please feel free to post back. Thanks!
Hi @Dmitry Petrov ,
According to my research, the Built-in protection preset security policy provides Safe Links protection to all recipients.
You could suggest your clients refer to this link to submit the URL that was falsely positived to Microsoft for analysis to create allow URL entries.
Or refer to the following link to create a Safe Links policy and add the URL that was falsely positived in “Do not rewrite the following URLs in email “section. This action will allow access to specific URLs that would otherwise be blocked by Safe Links.
Set up Safe Links policies in Microsoft Defender for Office 365 - Office 365 | Microsoft Learn
If the answer is helpful, please click "Accept Answer" and kindly upvote it. If you have extra questions about this answer, please click "Comment".
Note: Please follow the steps in our documentation to enable e-mail notifications if you want to receive the related email notification for this thread.
Thank you for the response! I think this can be marked as an accepted answer, however it's just a workaround.
We've tried reporting the url via ms security center and our requests simply disappear from the dashboard after a while, no effect on Safe Links, which tells me that appeal process does not work.
In general, reporting false positives to microsoft made absolutely no difference in our case
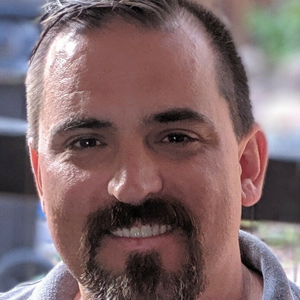
A new SafeLinks policy with a list of URLs to not re-write and applied to a subset of users or domains is supposed to fix this issue, although I have never seen it actually work in practice. Microsoft replaced the global settings in safe links with the TABL (Tenant Allow/Block Lists) and the method of allowing a URL is done via submitting in the TABL interface. If you already have a custom SafeLinks policy outside of the built-in protections, edit the protection settings and add the URL(s) to the Do not rewrite section.
In a pinch, you can also set up a transport rule in Exchange to bypass SafeLinks processing for certain users, or exclude them from existing policy. Neither is ideal for security purposes obviously.
Lastly, there are lots of SafeLinks URL decoders online you can search for and use to decode the URL and provide to end users, also as a temporary workaround in order to keep your users working.