' cx='32' cy='32' r='32' /%3E%3Ctext x='50%25' y='55%25' dominant-baseline='middle' text-anchor='middle' fill='%23FFF' %3EDO%3C/text%3E%3C/svg%3E)

' cx='32' cy='32' r='32' /%3E%3Ctext x='50%25' y='55%25' dominant-baseline='middle' text-anchor='middle' fill='%23FFF' %3EFD%3C/text%3E%3C/svg%3E)
' cx='32' cy='32' r='32' /%3E%3Ctext x='50%25' y='55%25' dominant-baseline='middle' text-anchor='middle' fill='%23FFF' %3EM%3C/text%3E%3C/svg%3E)
' cx='32' cy='32' r='32' /%3E%3Ctext x='50%25' y='55%25' dominant-baseline='middle' text-anchor='middle' fill='%23FFF' %3EGI%3C/text%3E%3C/svg%3E)
' cx='32' cy='32' r='32' /%3E%3Ctext x='50%25' y='55%25' dominant-baseline='middle' text-anchor='middle' fill='%23FFF' %3ELM%3C/text%3E%3C/svg%3E)
Hello @mensa84 et al.,
I think that I understand at an abstract level what is going wrong. In the trace there are 127 retransmissions: 94 fast retransmits and 33 normal retransmits. Each retransmission causes the "congestion window" to close a little (and, therefore, the throughput to be reduced). Most of the "fast retransmissions" are "spurious" (were not actually needed). WireShark "Expert Information" shows:
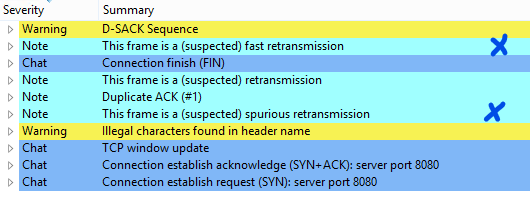
Both "fast retransmission" and "spurious retransmission" are mentioned. Here is a more detailed view of what is happening:
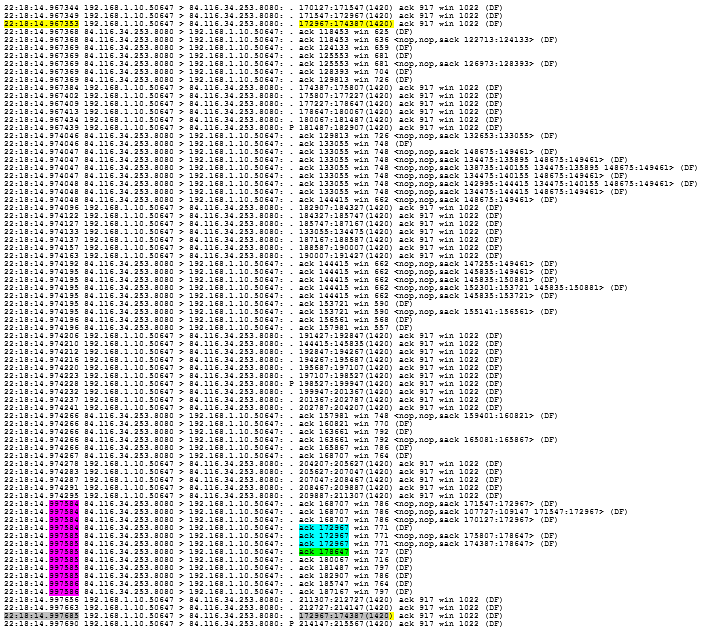
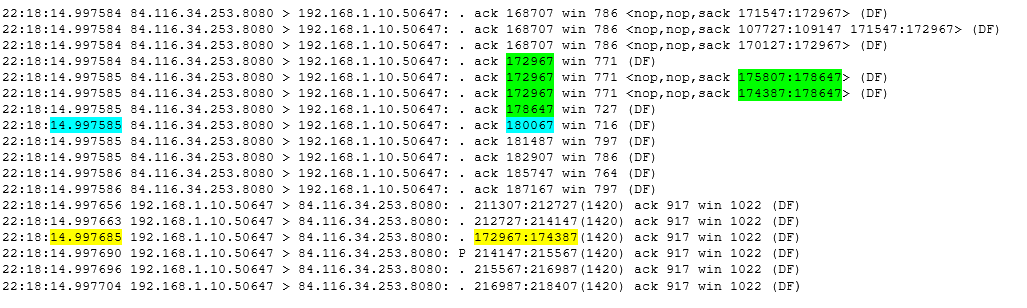
At 22:18:14.967353 the byte range 172967:174387 is transmitted for the first time.
Between 22:18:14.997584 and 22:18:14.997586 (30.231 milliseconds after the above and within a 2 microsecond period), 12 acknowledgements appear in the event trace (they have probably been "collected" by a lower level and then "indicated" as a group).
At this point in the trace, one estimate of "Round Trip Time" (RackMinRtt) is 18.994 milliseconds. Either the three occurrences of 172967 as the next "unacknowledged" sequence number (simple duplicated acknowledgement threshold) or a combination of this with "recent acknowledgement" ("rack") timings suggest that a "fast retransmission" would be apposite. This happens before the next packet is examined a few nanoseconds later, showing that the "missing" byte range has been acknowledged.
These images of the Microsoft-Windows-TCPIP trace data show that the packets arrive as a group and that, subsequently, a fast retransmission occurs:
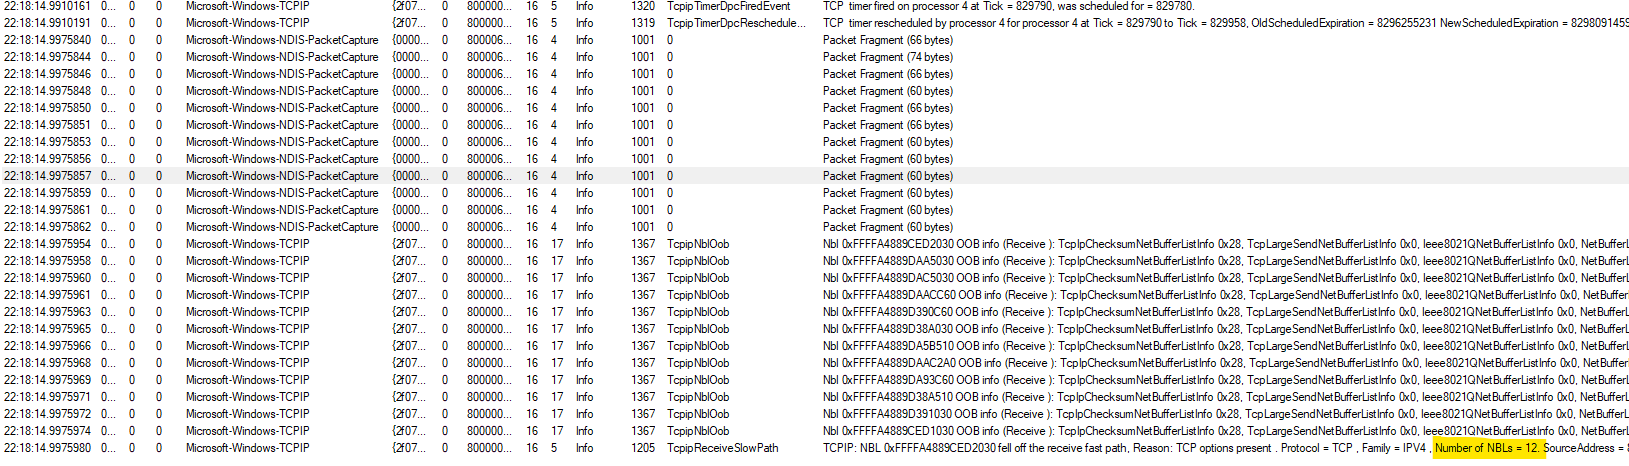

It is the high degree of "out-of-order" delivery of TCP segments (i.e. segments that are not received in the same order/sequence as which they were sent in) which perhaps limits the number of users who experience this behaviour.
I don't yet fully understand what can be done to influence this behaviour. Setting (in the registry) TcpMaxDupAcks to 3 might help (see https://learn.microsoft.com/en-us/troubleshoot/windows-server/networking/description-tcp-features) but, beyond that; I don't currently have any suggestions.
Another question is whether this behaviour has any impact on one's typical workload. It certainly substantially slows "streaming" of data to a server (as happens when posting data to a web server - this is what many "speed tests" measure), but it might have less (or no) impact when uploading data to a file share using SMB encapsulated in a VPN connection (in a "working from home" scenario) - the command/response nature of such transfers (and perhaps the fact that the "top level" protocol is Encapsulating Security Payload (ESP) rather than TCP) might slow down all devices/OSs to approximately the same level.
Gary

' cx='32' cy='32' r='32' /%3E%3Ctext x='50%25' y='55%25' dominant-baseline='middle' text-anchor='middle' fill='%23FFF' %3EMM%3C/text%3E%3C/svg%3E)