
I have seen this for a couple of years now. several end points...no issues were reported.
no solution,
This browser is no longer supported.
Upgrade to Microsoft Edge to take advantage of the latest features, security updates, and technical support.
' cx='32' cy='32' r='32' /%3E%3Ctext x='50%25' y='55%25' dominant-baseline='middle' text-anchor='middle' fill='%23FFF' %3EMO%3C/text%3E%3C/svg%3E)
Hey guys,
I've created restrictions on our client devices so that they are only allowed to use TLS 1.2
Now in the event viewer i see tons of error messages:
"A fatal error occurred while creating a TLS client credential. The internal error state is 10013."
From a couple of google search (primarily https://learn.microsoft.com/en-us/dotnet/framework/network-programming/tls#systemdefaulttlsversions) i've tried the following:
Creating the TLS 1.2 key: HKEY_LOCAL_MACHINE\SYSTEM\CurrentControlSet\Control\SecurityProviders\SCHANNEL\Protocols\TLS 1.2
Create subkeys for Client and Server with: DisabledByDefault 0 & Enabled 1
Created dword entries for .net 32 and 64 bit: 'HKLM:\SOFTWARE\WOW6432Node\Microsoft.NETFramework\v4.0.30319' / 'HKLM:\SOFTWARE\Microsoft.NETFramework\v4.0.30319' -name 'SystemDefaultTlsVersions' -value '1' and SchUseStrongCrypto '1' - Steps repeated for each .net framework key v1.0, v2.0.50727 and forth.
As an example
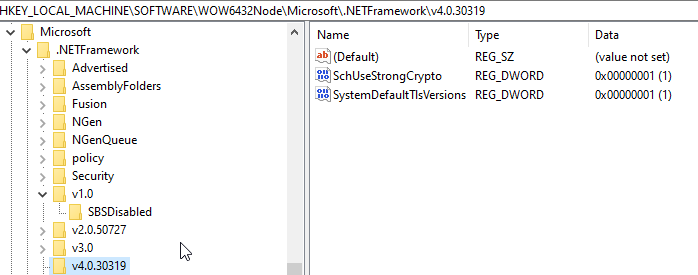
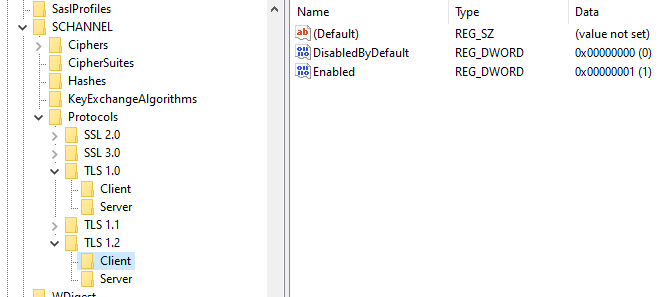
Our devices are running Windows 10 Enterprise edition. I've tried to test the changes on my device which is running 20H2.
Anyone with an idea of how i can proceed with the troubleshooting?
' cx='32' cy='32' r='32' /%3E%3Ctext x='50%25' y='55%25' dominant-baseline='middle' text-anchor='middle' fill='%23FFF' %3EMA%3C/text%3E%3C/svg%3E)
Hi,
the value in the TLS 1.2/Client MUST BE ffffffff in Hex or (4294967295) in decimal.
' cx='32' cy='32' r='32' /%3E%3Ctext x='50%25' y='55%25' dominant-baseline='middle' text-anchor='middle' fill='%23FFF' %3EAS%3C/text%3E%3C/svg%3E)
@Miguel Angel Crespo The Hex value of ffffffff for the DisabledByDefault or Enabled KEY?
' cx='32' cy='32' r='32' /%3E%3Ctext x='50%25' y='55%25' dominant-baseline='middle' text-anchor='middle' fill='%23FFF' %3EJK%3C/text%3E%3C/svg%3E)
Is there documentation or other sources for "ffffffff in Hex or (4294967295)"?
https://learn.microsoft.com/en-gb/dotnet/framework/network-programming/tls?WT.mc_id=Portal-Microsoft_Azure_Security#configuring-schannel-protocols-in-the-windows-registry Stated 1 to be correct value for DisabledByDefault and Enabled
' cx='32' cy='32' r='32' /%3E%3Ctext x='50%25' y='55%25' dominant-baseline='middle' text-anchor='middle' fill='%23FFF' %3ENM%3C/text%3E%3C/svg%3E)
@Janne Kujanpää
The documentation conflicts you can find both 1 and ffffffff in MS Documents.
What I can tell you is that the ffffffff value is what is set by Nartac's IIS Crypto.
I decided to run a test on my own machine and setting 1 for enabled caused TLS to fail in my browser. Putting it back to ffffffff removed the problem.
' cx='32' cy='32' r='32' /%3E%3Ctext x='50%25' y='55%25' dominant-baseline='middle' text-anchor='middle' fill='%23FFF' %3EN%3C/text%3E%3C/svg%3E)
If you are using Centralized Certificate Store the service account you configured it to use needs "Log on as batch job" rights.
secpol.msc -> Local Policies -> User Rights Assignment -> Log on as batch job -> add your service account
' cx='32' cy='32' r='32' /%3E%3Ctext x='50%25' y='55%25' dominant-baseline='middle' text-anchor='middle' fill='%23FFF' %3EE%3C/text%3E%3C/svg%3E)
I have seen this for a couple of years now. several end points...no issues were reported.
no solution,
No issues reported isn't the same as there isn't a problem.
I am seeing 36871 errors on most of my Win10 Clients. I am also seeing slow response in multiple web based 365 apps. None of my end users is saying much about this because they assume it is normal behaviour.
I note https://answers.microsoft.com/en-us/msoffice/forum/all/event-id-36871schannel-repeating-tls-error-10016/dd7070ce-216f-4100-8d23-0fe32af376f5 indicates that can cause issues with even local network calls to an MS access database and might be a cause of delayed reports and points to the deprecation of TLS 1.0.
Interestingly the issue of applications that use Azure AD and this TLS deprecation is mentioned here too. https://learn.microsoft.com/en-us/troubleshoot/azure/active-directory/enable-support-tls-environment?tabs=azure-monitor
That article contains an interesting note
"Note
By default, an OS that supports TLS 1.2 (for example, Windows 10) also supports legacy versions of the TLS protocol. When a connection is made by using TLS 1.2 and it doesn't get a timely response, or when the connection is reset, the OS might try to connect to the target web service by using an older TLS protocol (such as TLS 1.0 or 1.1). This usually occurs if the network is busy, or if a packet drops in the network. After the temporary fallback to the legacy TLS, the OS will try again to make a TLS 1.2 connection.
What will be the status of such fallback traffic after Microsoft stops supporting the legacy TLS? The OS might still try to make a TLS connection by using the legacy TLS protocol. But if the Microsoft service is no longer supporting the older TLS protocol, the legacy TLS-based connection won't succeed. This will force the OS to try the connection again by using TLS 1.2 instead."
Could it be that the slow response from 365 applications that use the web like Sharepoint, Onedrive and Outlook are down to a busy network and fall back to deprecated protocols? If so then it explains the numerous 36871 errors being logged on my Win10 clients.
' cx='32' cy='32' r='32' /%3E%3Ctext x='50%25' y='55%25' dominant-baseline='middle' text-anchor='middle' fill='%23FFF' %3ETT%3C/text%3E%3C/svg%3E)
Still error, no help.
Microsoft, please fix it.
There is an issue with the Microsoft documentation on enabling TLS and other security protocols.
Older documentation shows setting via registry key needs a DWORD enabled = 1
later documentation shows the DWORD enabled = ffffffff
I have tested it recently and enabled =1 did not work it had to be ffffffff.
Nartac's IIS Crypto GUI app also sets ffffffff . Try using that app https://www.nartac.com/Products/IISCrypto/Download
to set your servers and clients to Best Practices and rebooting. See if that helps.
However, I am finding some articles online that show the errors can also be logged when a slow network response causes the client to fall back to a deprecated version of TLS before 1.2 despite TLS 1.2 being correctly enabled.
Note
By default, an OS that supports TLS 1.2 (for example, Windows 10) also supports legacy versions of the TLS protocol. When a connection is made by using TLS 1.2 and it doesn't get a timely response, or when the connection is reset, the OS might try to connect to the target web service by using an older TLS protocol (such as TLS 1.0 or 1.1). This usually occurs if the network is busy, or if a packet drops in the network. After the temporary fallback to the legacy TLS, the OS will try again to make a TLS 1.2 connection.
What will be the status of such fallback traffic after Microsoft stops supporting the legacy TLS? The OS might still try to make a TLS connection by using the legacy TLS protocol. But if the Microsoft service is no longer supporting the older TLS protocol, the legacy TLS-based connection won't succeed. This will force the OS to try the connection again by using TLS 1.2 instead.
' cx='32' cy='32' r='32' /%3E%3Ctext x='50%25' y='55%25' dominant-baseline='middle' text-anchor='middle' fill='%23FFF' %3EKW%3C/text%3E%3C/svg%3E)
Hi everyone, some state the value has to be 0xffffffff instead of 0x1 (Decimal 1)
Nartac however patched their product with the following note
Version 3.2 Build 16 - Released April 11, 2020
The referred guidance still shows that value of one is correct. Where did you see documentation changed to the other value?
The Enabled value data in these registry keys under the Protocols key takes precedence over the grbitEnabledProtocols value that is defined in the SCHANNEL_CRED structure that contains the data for a Schannel credential. The default Enabled value data is 0xffffffff.
See what I mean about conflicting.
I have tested in my environment and 1 does break our connections
' cx='32' cy='32' r='32' /%3E%3Ctext x='50%25' y='55%25' dominant-baseline='middle' text-anchor='middle' fill='%23FFF' %3EAS%3C/text%3E%3C/svg%3E)
I encountered this error when I tried to run the Microsoft Store and Xbox apps on my Windows 11 Home 25H2.
In the System Events I saw the message:
A fatal error occurred while creating a TLS client credential. The internal error state is 10013.
This issue was resolved by enabling TLS 1.2.
The simplest way to do this is through Internet Properties pane:
Win + Rinetcpl.cpl and press EnterAdvanced tabSecurity section check Use TLS 1.2Additionally, for security reasons, it is recomended to:
TLS 1.3The registry values mentioned in previous comments are correct, however, the registry entries themselves should not exist by default.