Anomaly in applying password policies to DCs

2026-09-17T10:35:04.3566667+00:00

ad pASSWORD

Hello, colleagues!

Has anyone by any chance resolved this strange anomaly?

I have two AD sites, one of which has two DC WS 2022 GUIs in the Yandex Cloud.

The other two DC WS 2022 Cores are in the site at the DC.

On August 31, the Maximum password age setting in the Default Domain Policy was changed from 0 to 180 days on the DC with the PDC role.

But a little later, while running one of the scripts, discrepancies in the account parameters were discovered:

DC attribute msDS-UserPasswordExpiryTimeComputed

YA-DC01 9223372036854775807

YA-DC02 9223372036854775807

9223372036854775807 -> 0x7FFFFFFFFFFFFFFFF, which is the special value "password never expires"

SL-dc03 134364635281752932

SL-dc04 134364635281752932

However, the DC in the DC correctly calculates 134364635281752932 from the same pwdLastSet.

The Default Domain Password Policy object in AD is correct for the entire domain: Maximum password age = 180.

BUT on the DC in the cloud!

YA-DC01/YA-DC02

MaxPasswordAgeRaw: -1

MaxPasswordAgeDays: TIMEQ_FOREVER

This means that the local SAM of these two DCs calculates:

maximum password age = forever.

And net accounts on YA also show:

Maximum password age (days): Unlimited

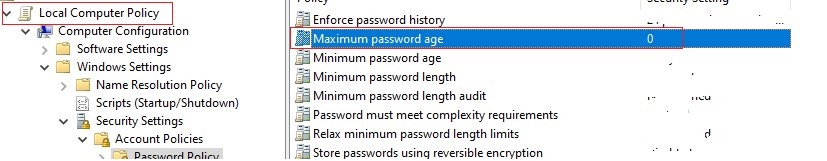
Local Security Policy on YA-DC01/YA-DC02 (i.e., the local policy settings on these DCs in YA) - Maximum password age: 0 days

This was verified:

pwdLastSet is the same; ✅

userAccountControl = 512;✅

msDS-ResultantPSO missing;✅

FGPP not applied;✅

AD and SYSVOL replication verified;✅

Default Domain Policy applied;✅

SceCli reports successful policy application.✅

We compared versions and KBs, but there's no confirmed Microsoft issue/KB for this specific case yet.✅

I see it this way: the problem isn't with AD or SYSVOL replication. On two YA-DCs, the local SAM/NetAPI state doesn't match the domain policy. This is why the same user receives different password expiration calculations depending on the DC.

In short, the local policy on both DCs (in the cloud) shows the following after applying the required password policy (screenshot attached). There are no other policies affecting the local policy—I've also verified this.

I can't recall a problem like this in many years. I laid it out as best I could. Can anyone tell me, or is it possible the box just opens?

Windows for business | Windows Server | Directory services | Active Directory
0 comments No comments

3 answers

Sort by: Oldest
  1. Marcin Policht 108.9K Reputation points MVP Volunteer Moderator
    2026-09-17T11:08:06.96+00:00

    You have done excellent work ruling out nearly all typical failure points (SYSVOL, FGPP, PSOs, and SceCli).

    Consider running the following on one of the affected DCs (and reboot it afterwards) -

    secedit /configure /cfg %windir%\inf\defltbase.inf /db defltbase.sdb /verbose

    gpupdate /force


    If the above response helps answer your question, remember to "Accept Answer" so that others in the community facing similar issues can easily find the solution. Your contribution is highly appreciated.

    hth

    Marcin

    Was this answer helpful?

    0 comments No comments

  2. Harry Phan 32,265 Reputation points Independent Advisor
    2026-09-17T11:15:34.8+00:00

    Hello Dmitry,

    What you are seeing is indeed an inconsistency between domain-level password policy enforcement and the local SAM/NetAPI state on the two cloud-based DCs. The fact that MaxPasswordAgeRaw is showing -1 (TIMEQ_FOREVER) on YA-DC01/02 while the Default Domain Policy is correctly set to 180 days strongly suggests that those DCs are not correctly interpreting or applying the domain password policy, even though replication and policy application logs look fine.

    The critical point here is that domain password policies are not applied through local security policy objects on DCs. Instead, they are enforced by the domain controllers themselves via the Default Domain Policy. When you see “Maximum password age: Unlimited” in net accounts on a DC, that reflects the local SAM policy, not the effective domain password policy. Normally, on DCs, the local SAM values are irrelevant because domain accounts are governed by domain policy. The anomaly is that your cloud DCs are exposing the SAM values as if they were authoritative, which leads to the discrepancy in msDS-UserPasswordExpiryTimeComputed.

    This behavior has been observed in certain builds of Windows Server 2022 where the local SAM policy on DCs can incorrectly override or misreport domain password policy values. Microsoft has not yet published a KB specific to this, but the recommended approach is to ensure that the Default Domain Policy is the only policy defining password settings, and to avoid configuring password policies in Local Security Policy on DCs. In practice, you should confirm that no local GPOs or baseline hardening templates were applied on YA-DC01/02 that might have set Maximum password age = 0. Even if you see “successful application” in SceCli, the local policy object may still be persisting a conflicting setting.

    The immediate remediation is to reset the local security policy on those DCs so that they inherit only domain-level settings. Run secedit /configure /cfg %windir%\inf\defltbase.inf /db defltbase.sdb /verbose on YA-DC01 and YA-DC02 to restore the default local security policy baseline. After that, force a GPUpdate and reboot. Then recheck net accounts and msDS-UserPasswordExpiryTimeComputed. The values should align with the domain policy (180 days).

    If the anomaly persists even after resetting local policy, you are likely hitting a product bug in Server 2022’s handling of SAM policy on DCs. In that case, the only reliable path forward is to open a support case with Microsoft CSS, as they can provide hotfixes or confirm whether this is a known issue in your build.

    I hope you've found something useful here. If it helps you get more insight into the issue, it's appreciated to accept the answer. Should you have more questions, feel free to leave a message. Have a nice day!

    HP.

    Was this answer helpful?

    0 comments No comments

  3. Дмитрий Макаров 0 Reputation points
    2026-09-17T11:46:02.92+00:00

    Thanks, guys. I'll definitely report back once I've done it!

    But while we're in the process of changing the password lifetime to 90 days, I wouldn't skip it right now to avoid another policy enforcement conflict and impact on end users.

    Was this answer helpful?

    0 comments No comments

Your answer

Answers can be marked as 'Accepted' by the question author and 'Recommended' by moderators, which helps users know the answer solved the author's problem.