I'm running Windows 11 Pro 25H2 as a Type 2 Hyper-V VM. The C: drive is Bitlocker protected with keys stored in the vTPM.
I have many files and directories on two disks, W: and X:, that are EFS encrypted. I can open and read the files no matter which disk they are on; however, I cannot 'decrypt in place' files located on the W: drive but I can for files located on the X: drive.
At the top level, the two disks appear to me to have the same security provisions.
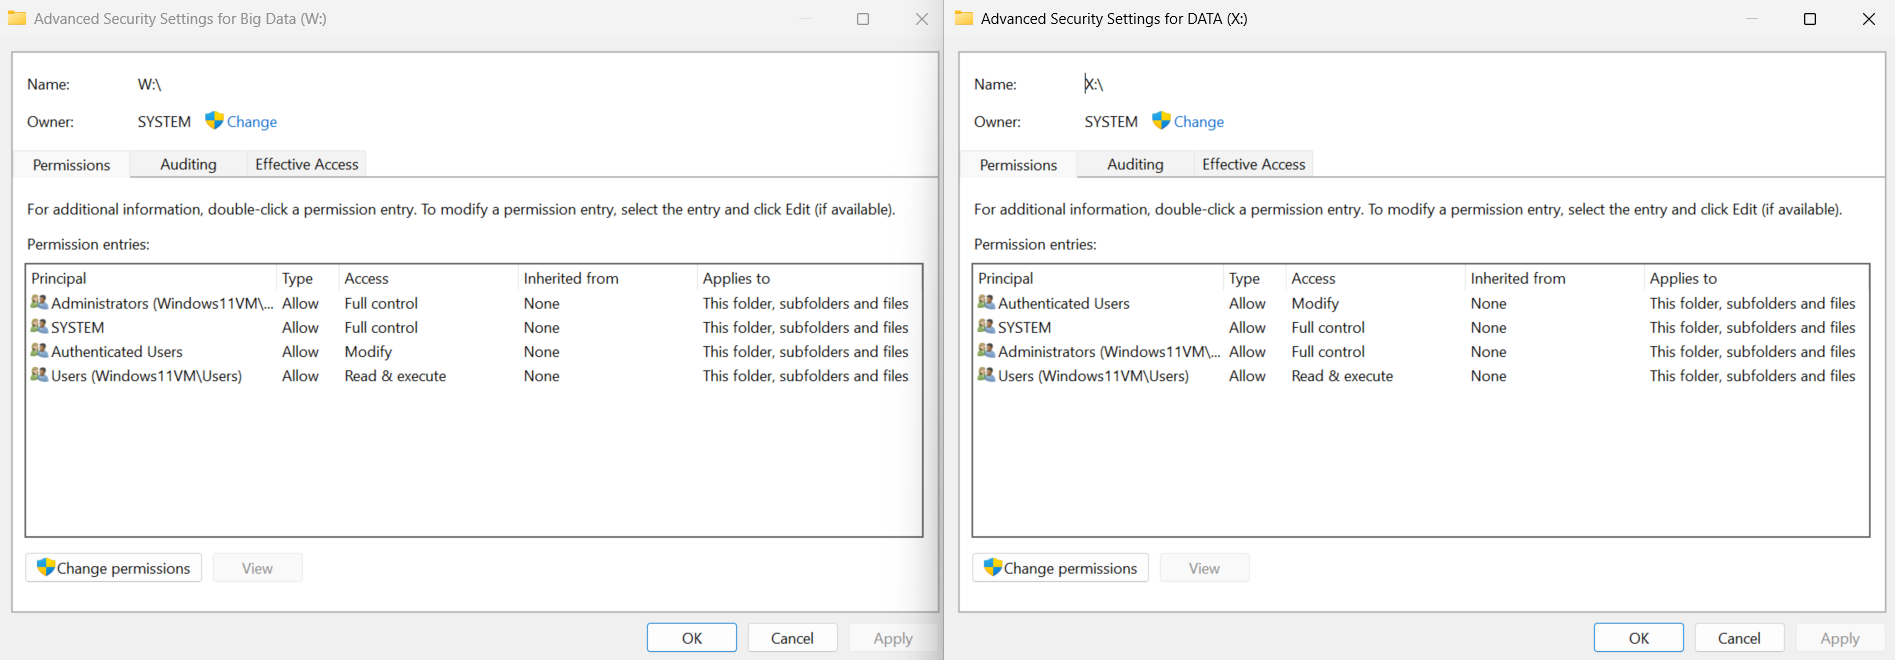
If I place an encrypted file, TestFile.mp4, in the root directory of X: and attempt to unencrypt it, the operations works as expected. However, if I place the same file in the root directory of W: and attempt to unencrypt it, the operation first wants me to use Administrator privileges and once those are granted, it fails to decrypt. (And again, I can read the file no matter which disk it is on, I just can't decrypt in place on W:.)
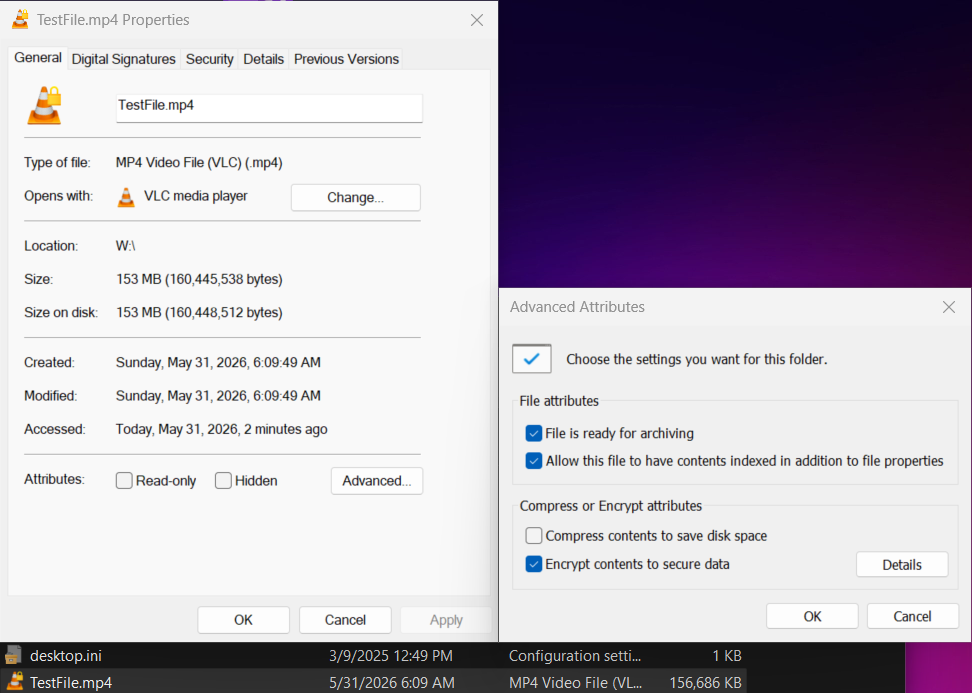
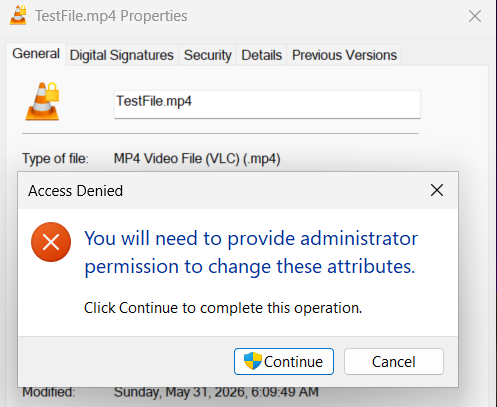
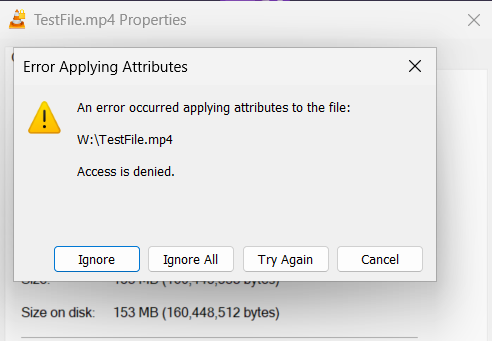
The file is owned by me and I am a member of the Administrators group. I can open the file, read the file, copy the file, delete the file, rename the file... as best I can tell I can do everything except unencrypt the file in place on the W: drive.
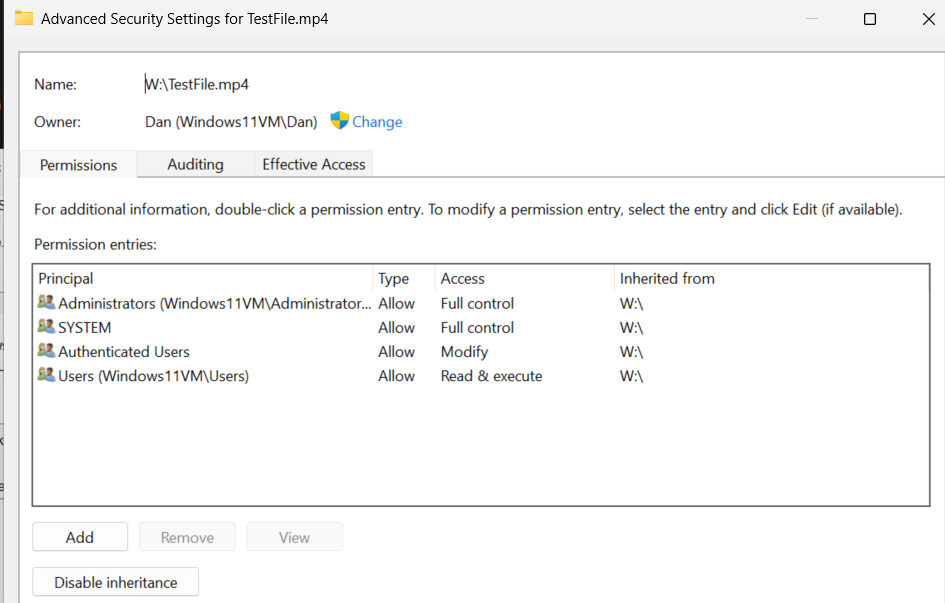
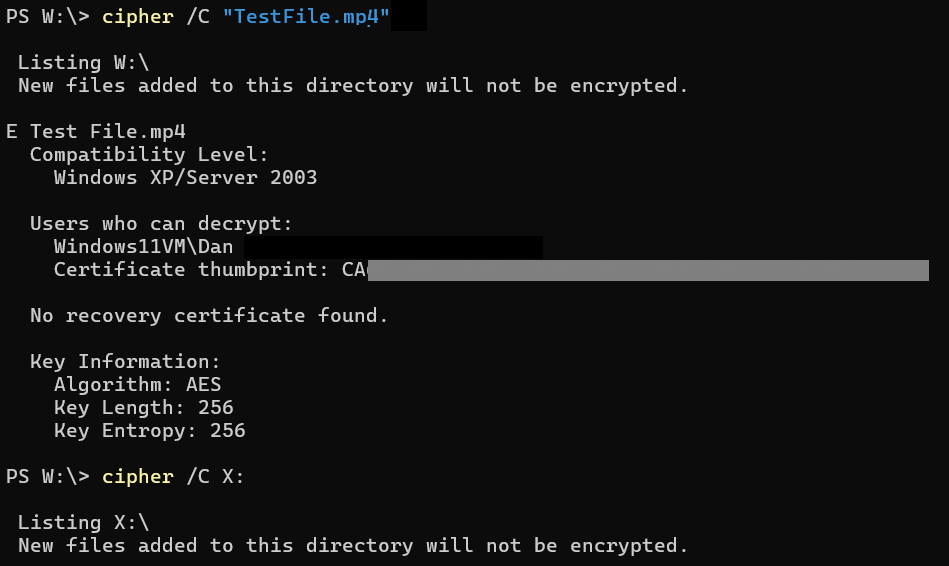
And now I confess how I got to this point. After installing KB5089573 on the host OS, the VM refused to boot saying it couldn't find any operating systems to boot. So I built a new VM and attempted to access the disks from the new instance. Of course there were a lot of issues with ownership and permissions that I attempted to address with reckless use of Takeown and icacls before realizing I was also going to need the EFS certificate on the new machine. Fortunately I had the EFS certificate saved in an accessible location; unfortunately I did not remember the password for the pfx file. So I turned back to trying to searching the internet for clues how to boot the original system.
I eventually stumbled on a combination of disabling Secure Boot and (fortunately) having the Bitlocker recovery key for the VM's C: disk available and was able to boot the original system. But now it is working with W: and X: drives where I have been screwing around with file and directory ownership and ACLs.
Lastly, there is another issue that I believe is related, though I have no idea how (it certainly started at the same time). The Windows Search service cannot see, and thus will not index, the W: drive, though it can see the X: drive. I've used the Modify and Show all locations buttons in the Indexing Options window. Both disks have checked 'Allow files on this drive to have contents indexed in addition to file properties'. But the W: drive is invisible to Search.
So... any wizards out there with suggestions on how to restore normal behavior -- both to EFS decryption and Windows Search?
' cx='32' cy='32' r='32' /%3E%3Ctext x='50%25' y='55%25' dominant-baseline='middle' text-anchor='middle' fill='%23FFF' %3EL%3C/text%3E%3C/svg%3E)

' cx='32' cy='32' r='32' /%3E%3Ctext x='50%25' y='55%25' dominant-baseline='middle' text-anchor='middle' fill='%23FFF' %3EV%3C/text%3E%3C/svg%3E)