Upon inspecting your security event logs, the Process tracking audit seems enabled, although you've cleared the audit policies by running the "auditpol.exe /clear" command.
Please re-run these commands:
- auditpol.exe /clear
- auditpol.exe /get /category:* >c:\audit.txt
- secedit.exe /export /areas SECURITYPOLICY /cfg c:\audit_legacy.txt
- reg export "HKLM\SYSTEM\CurrentControlSet\Services\EventLog\Security" c:\eventlog.reg
Upload C:\audit.txt, C:\audit_legacy.txt, and C:\eventlog.reg.
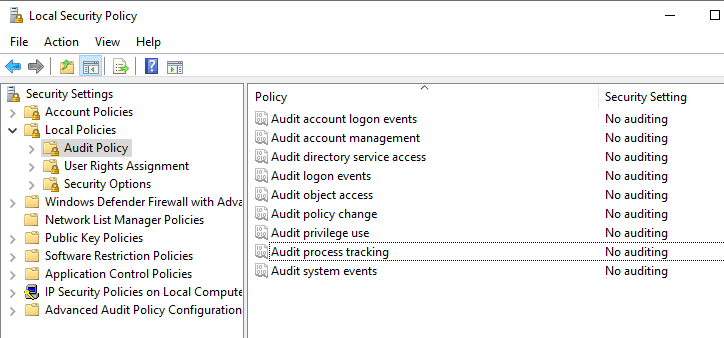
Open secpol.msc and set everything to "No auditing" on the Audit Policy page.
//A solution within a next WU-update , is possible still ( ?)//
I think you may report this in the Feedback tool... it might get substantial upvotes.
' cx='32' cy='32' r='32' /%3E%3Ctext x='50%25' y='55%25' dominant-baseline='middle' text-anchor='middle' fill='%23FFF' %3EA%3C/text%3E%3C/svg%3E)

