The Local Security Authority protection is off - Windows 11 Home

Anonymous
2023-03-17T06:10:20+00:00

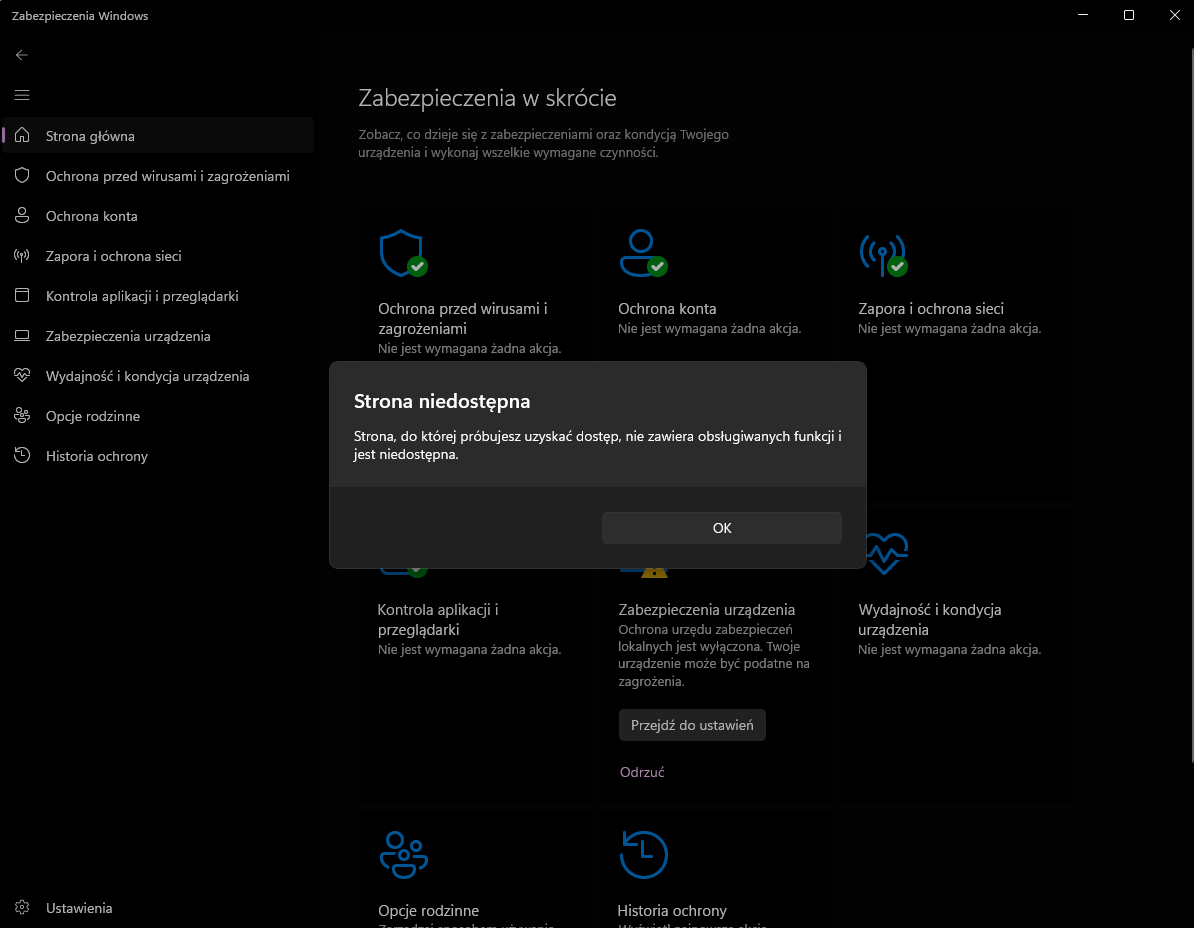
A yellow triangle appeared on the Windows Security iron yesterday. It says that Local Security Authority protection is off. Your device may be vulnerable.

I can press Go to settings or Dismiss but when I click go to settings, a notification saying "the page You want to access doesn't contain required functions and is unavailable". 

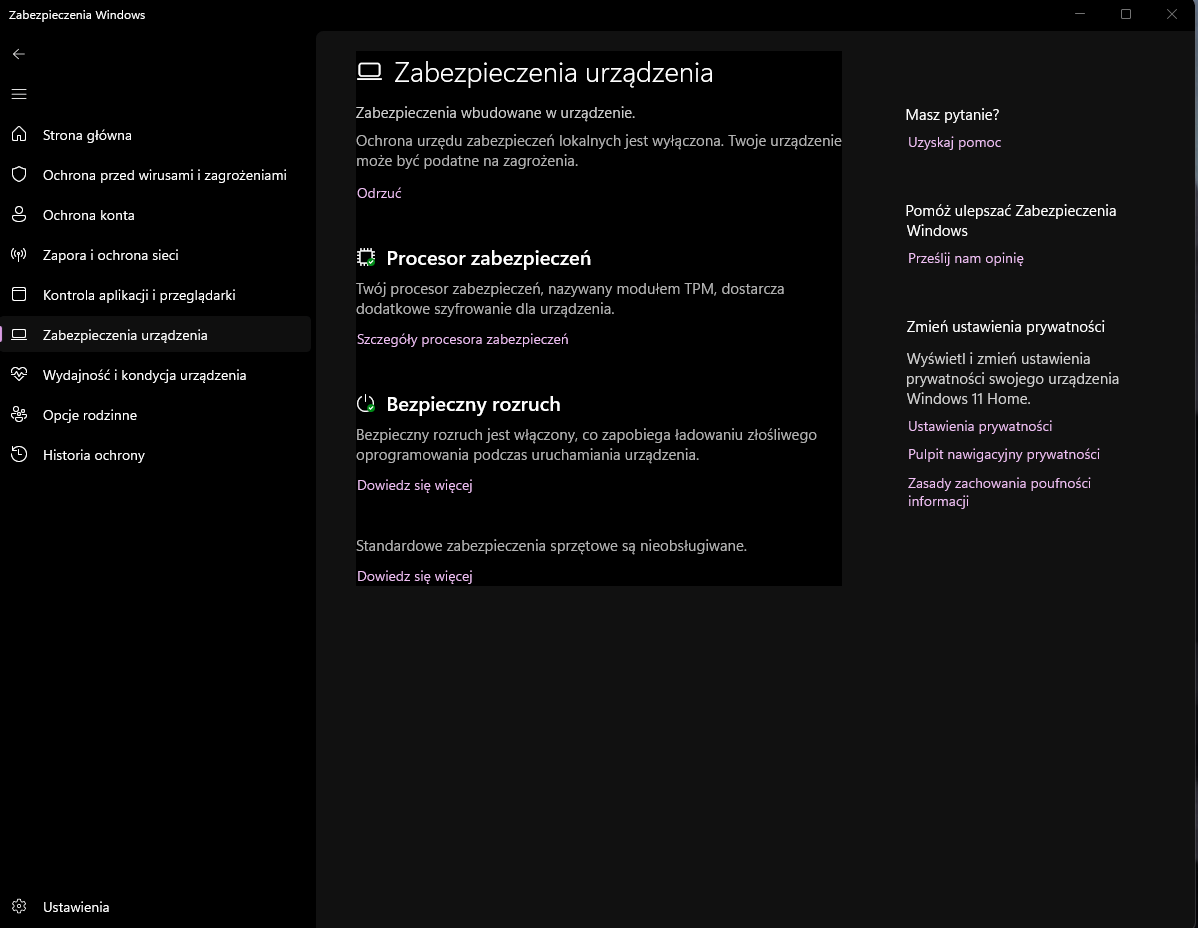
There is also no option to turn the protection on in the Device Security panel (there is only "dismiss" option).

When I was looking at it yesterday, there was also a notification that "The tpm module is unavailable" but today it doesn't show. I checked the device manager and uefi and both say that the tpm is enabled.

I've found an advice to turn on SMV in UEFI (in the CPU settings) to solve the problem but I don't want to change anything in BIOS without consultation as I'm no expert. I've also found a reply from a truste source that this whole problem is a Microsoft bug and it's better to just wait till they fix it.

What should I do?

Screenshots are in Polish, I hope they can be useful somehow. The first one shows the notification about a page being not available and the second shows the Device security panel (the notification from the first screenshot displays when I close the device security page or when I click on "go to settings" below the information that the protection is turned off). There is also an information (second screenshot) that "standard device security is not supported".
Windows for home | Windows 11 | Security and privacy

Locked Question. This question was migrated from the Microsoft Support Community. You can vote on whether it's helpful, but you can't add comments or replies or follow the question.

0 comments No comments
Answer accepted by question author
Anonymous
2023-07-06T07:36:56+00:00

Microsoft have just posted that they have resolved the "Local Security Authority protection is off" issue in an update. Has anyone tried to apply it from Windows Update?

Resolution: This issue was resolved in an update for Windows Security platform antimalware platform KB5007651 (Version 1.0.2306.10002). If you would like to install the update before it is installed automatically, you will need to check for updates.

Was this answer helpful?

10+ people found this answer helpful.
0 comments No comments

174 additional answers

Sort by: Oldest
  1. Deleted

    This answer has been deleted due to a violation of our Code of Conduct. The answer was manually reported or identified through automated detection before action was taken. Please refer to our Code of Conduct for more information.


    Comments have been turned off. Learn more

  2. Anonymous
    2023-05-19T08:09:39+00:00

    Hello Cory Royce,

    You sayd " Microsoft have explicitly told people not to apply any workarounds other than clicking dismiss " ,

    and that's what Microsoft advises and there are supporters in favor of this attitude, but there are other specialists who recommend to create these 2 registry values RunAsPPL and RunAsPPLBoot in D Word 32 bits by giving them a value of 2 and who say that if you don't, there is no kernel protection.

    No one can affirm or prove 100% what is best in terms of security, so we are all in a dark smoke.

    The reason why that there has been no real fix for this , and no fix for the mail app in Windows 11 , is i suspect that the big push moving forward is Windows 12 , and that all essential staff have been moved onto Windows 12 for the big push, yes purely speculation on my part, but not a completely unrealistic scenario

    Was this answer helpful?

    0 comments No comments
  3. Anonymous
    2023-05-19T11:14:41+00:00

    From the people I have talked to including computer experts if you are running a third party antivirus such as norton you are fineFrom the people I have talked to including computer experts if you are running a 3rd party antivirus such as Norton you are fine and cand can simply. Dismiss the warning and go on about your business.

    Was this answer helpful?

    1 person found this answer helpful.
    0 comments No comments
  4. Anonymous
    2023-05-19T13:46:37+00:00

    Bonjour,

    J'ai fait cette procédure ci recommandée par Microsoft ->

    https://learn.microsoft.com/fr-fr/windows-server/security/credentials-protection-and-management/configuring-additional-lsa-protection?utm_source=pocket_saves , je vous en met un bref extrait :

    "Comment activer la protection LSA sur un seul ordinateur

    Utilisation du Registre

    1. Ouvrez l'Éditeur du Registre (RegEdit.exe) et accédez à la clé de Registre qui se trouve à l'emplacement suivant : HKEY_LOCAL_MACHINE\SYSTEM\CurrentControlSet\Control\Lsa.
    2. Affectez la valeur suivante à la clé de Registre :
      1. "RunAsPPL"=dword:00000001 pour configurer la fonctionnalité avec une variable UEFI.
      2. "RunAsPPL"=dword:00000002 pour configurer la fonctionnalité sans variable UEFI (uniquement sur Windows 11, 22H2).
    3. Redémarrez l'ordinateur."

    Il y a moyen de vérifier si la protection LSA est bien active tel encore que mentionné dans ce lien ->

    "Vérification de la protection LSA

    Pour déterminer si LSA a démarré en mode protégé au démarrage de Windows, recherchez l'événement WinInit suivant dans le journal Système sous Journaux Windows :

    • 12 : LSASS.exe a démarré en tant que processus protégé avec le niveau : 4" ,

    ... mais une fois sur 2 ça ne fonctionne pas ->

    "recherchez l'événement WinInit ( attention faute de frappe de Microsoft : c'est l'événement Wininit donc un i à la place du l ) suivant dans le journal Système sous Journaux Windows :

    • 12 : LSASS.exe a démarré en tant que processus protégé avec le niveau : 4" ,

    si Norton dit que ce n'est pas grâve je vais laisser cela comme ça et supprimer l'entrée D Word 32 bit RunAsPPL

    Was this answer helpful?

    0 comments No comments