Critical System Issues Following Windows 11 24H2 Update: Boot Errors, System Freeze, and Bitlocker Access Denied

Anonymous
2025-01-15T14:00:56+00:00

Two days back I received the Windows 11 24H2 Update on my system "HP Omen 16". Following the installation, I observed two identical entries for 'Windows 11 on volume 3' within the boot menu. No selection was made, and the system successfully logged into Windows after a 30-second delay.

The following workday, I consulted with our IT department regarding this behavior. Upon restarting the system in their presence, the dual boot entries reappeared. Attempts to select between the entries were unsuccessful. Proceeding to 'Change defaults or choose other options' and selecting the 'Repair' option resulted in a system freeze, characterized by an automatic reboot loop.

Subsequent attempts at system recovery using built-in tools encountered the following error:

"Your PC/Device needs to be repaired.

A required device isn't connected or can't be accessed.

Error Code: 0xc0000225"

![](https://learn-attachment.microsoft.com/api/attachments/d99e4b91-e430-4162-a12e-e9bb43699141?platform=QnA

Furthermore, accessing the Recovery Environment by pressing F1 also resulted in a system freeze and reboot loop.

Efforts to utilize a bootable USB drive for recovery were hindered by a request for the Bitlocker Encryption key. It is suspected that the Bitlocker keys may have been invalidated or altered during the Windows 11 24H2 update process, as previously saved keys are no longer functional.

Could anyone please advise/assist on how to proceed? Additionally, I’d like to confirm if there are any extra steps I should take to avoid BitLocker recovery issues while performing this.https://learn-attachment.microsoft.com/api/attachments/e8b5c6b5-ddd4-45e1-a55e-3e0f9b2c43f9?platform=QnA

Windows for home | Windows 11 | Windows update

Locked Question. This question was migrated from the Microsoft Support Community. You can vote on whether it's helpful, but you can't add comments or replies or follow the question.

0 comments No comments

48 answers

Sort by: Newest
  1. Anonymous
    2025-05-08T09:46:40+00:00

    I'd be definitely yes.

    Everytime syspreps, the boot entry will be modified to use boot file location as how windows boot manager identifies the OS.

    Hence, you'll need to run the below command to remediate the bcdedit config to the original settings.

    bcdedit /set {default} device partition=\Device\HarddiskVolume3

    bcdedit /set {default} osdevice partition=\Device\HarddiskVolume3

    Was this answer helpful?

    0 comments No comments
  2. Anonymous
    2025-04-29T18:05:03+00:00

    That's a good find. We have a small shop and use sysprep to create images. We use Dell Latitude laptops. For the past few years everything is fine. I created a new image using the win11 24h2 ISO and it works fine UNTIL i turn on bitlocker and then I get a blue screen with the SRTTRAIL.txt error pointing to the D:\recovery\windowsre...

    I tried to rebuild, fixmbr, sfc,.....all of it.

    If I did the above and got it to boot, won't a new sysprep fudge it up again?

    thanks
    DannyD

    Was this answer helpful?

    0 comments No comments
  3. Anonymous
    2025-03-24T10:54:03+00:00

    The exactly same issue happened to me. I had a fresh Windows 24H2 USB installation iso installed on my laptop. To test this out, I did sysprep once and pressed Shift+F10 and typed in the Bitlocker encryption command "manage-bde -on C: -rp -s" right after the first boot into oobe. Then I rebooted the system right after the Bitlocker is enabled.

    My laptop started to enter into Windows Recovery Environment at this time and is unable to boot in to normal Windows environment anymore.

    To temporarily solve this, I have to obtain the backup Bitlocker recovery key when Bitlocker in enabled before the issue happens. Then use the command prompt in windows recovery environment and type in "manage-bde -status" to obtain the boot drive name start with "\" and copy it. Then type in "manage-bde -unlock \BootDriveName -rp 48DigitBitLockerRecoveryKey" to unlock the boot drive. Last, type in "manage-bde -off \BootDriveName" to turn off Bitlocker (decrypt) on the boot drive. And I will be able to boot into Windows normally after a reboot.

    It's shocked that Windows 24H2 can just be easily destroyed with a Bitlocker encryption.

    This NEVER happens in previous Windows version (23H2, 22H2, 21H2...etc)

    Hey guys,

    I have an update with my final findings and solution regarding Windows 11 24H2 conflicts with Sysprep and Bitlocker!

    If you are looking for solution, you can just skip this part.

    All findings were investigated using "bcdedit" command line.

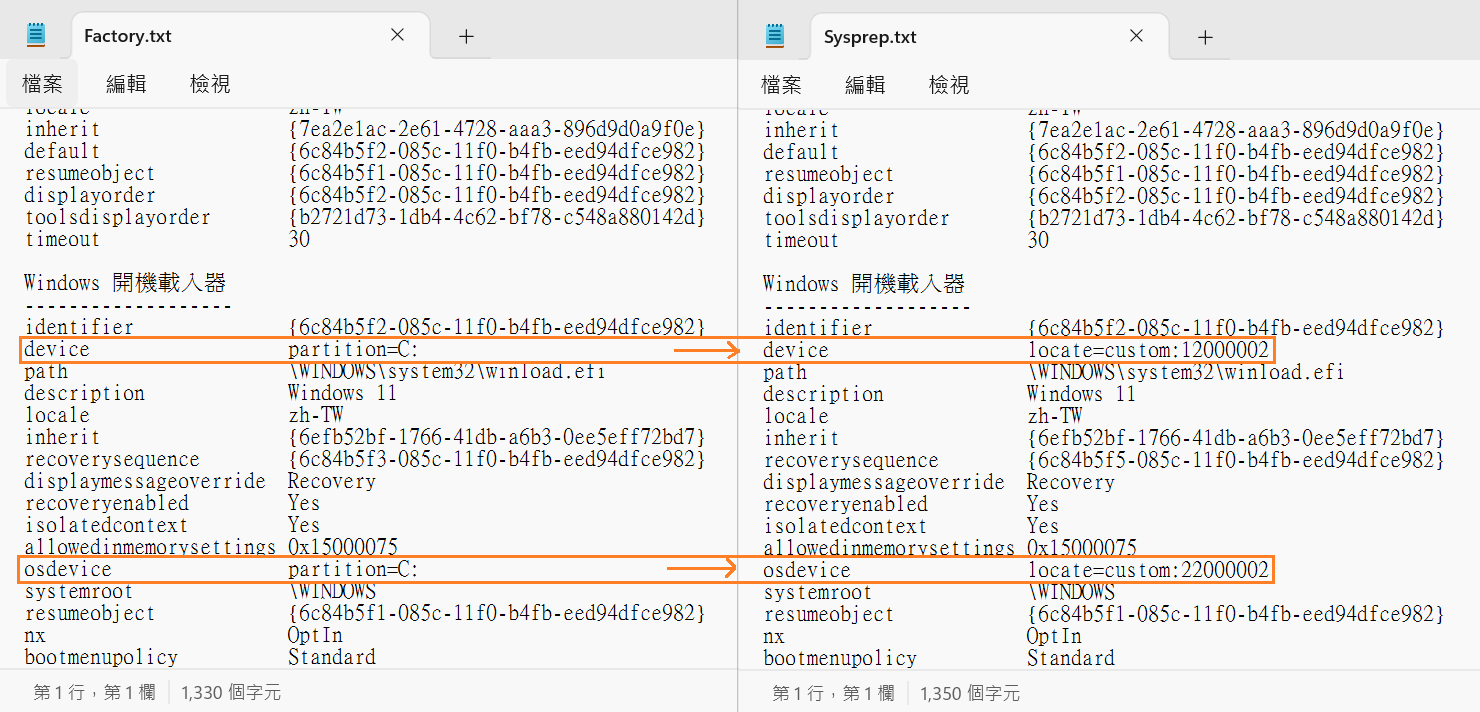
    I found that when sysprep is done under 24H2, "device" and "osdevice" attribute in default boot entry will be changed from "partition=C:" to "locate=custom:xxxxxxxx"

    I'm then curious about the content of "locate=custom:xxxxxxxx". It is showing as the value below in Windows recovery environment:

    device > locate=\Windows\system32\winload.efi

    osdevice > locate=\Windows
    Image

    After the above attributes are changed from "partition" to "locate" and as Bitlocker is turned-on on C: drive, windows boot manager cannot recognize the C: drive as the OS boot drive because sysprep changes the way Windows boot manager identifies boot entry. Since the OS drive was encryped by Bitlocker, Windows boot manager cannot locate the boot files. So that cause the windows boot manager fails to boot into Windows and goes to Windows recovery environment instead. No matter how many types of fixes suggested in Windows recovery environment won't help with this issue.

    Solution

    If you are able to boot into Windows recovery environment, you can access the command prompt by clicking the "Advanced Options" at Automatic Repair screen > Troubleshooting > Advanced Options > Command Prompt.

    In command prompt, type and run the below 2 commands

    bcdedit /set {default} device partition=\Device\HarddiskVolume3

    bcdedit /set {default} osdevice partition=\Device\HarddiskVolume3

    Usually the OS disk is on the partition "HarddiskVolume3". If you'd like to confirm which partition the OS is in, you can use the following commands to check:

    diskpart
    list disk
    select disk 0 (normally select the largest one)
    list part

    You can check if the 3rd partition is marking as the main disk (Normally the largest one)

    If you know which partition is your OS located, the \Device\HarddiskVolume? (? is the partition number of OS located in) command mentioned above **** should also be changed as well.

    If you are unable to enter the screen above, you may need to use a Windows installation/repair USB to boot up. Once your PC is boot up from USB, press Shift+F10 to run command prompt. Then perform the action mentioned above.

    After bcdedit /set command is done running, you should be able to close the command prompt and reboot normally in to the OS without losing your data.

    Was this answer helpful?

    1 person found this answer helpful.
    0 comments No comments
  4. Anonymous
    2025-03-18T16:17:23+00:00

    Thank you for your reply.

    I still don’t understand why Microsoft is not taking responsibility for this problem.

    They caused it and Microsoft should solve their problem they created.

    Poor customer service

    Apple doesn’t have these issues

    Cheers

    Was this answer helpful?

    3 people found this answer helpful.
    0 comments No comments
  5. Anonymous
    2025-03-18T13:56:38+00:00

    The exactly same issue happened to me. I had a fresh Windows 24H2 USB installation iso installed on my laptop. To test this out, I did sysprep once and pressed Shift+F10 and typed in the Bitlocker encryption command "manage-bde -on C: -rp -s" right after the first boot into oobe. Then I rebooted the system right after the Bitlocker is enabled.

    My laptop started to enter into Windows Recovery Environment at this time and is unable to boot in to normal Windows environment anymore.

    To temporarily solve this, I have to obtain the backup Bitlocker recovery key when Bitlocker in enabled before the issue happens. Then use the command prompt in windows recovery environment and type in "manage-bde -status" to obtain the boot drive name start with "\" and copy it. Then type in "manage-bde -unlock \BootDriveName -rp 48DigitBitLockerRecoveryKey" to unlock the boot drive. Last, type in "manage-bde -off \BootDriveName" to turn off Bitlocker (decrypt) on the boot drive. And I will be able to boot into Windows normally after a reboot.

    It's shocked that Windows 24H2 can just be easily destroyed with a Bitlocker encryption.

    This NEVER happens in previous Windows version (23H2, 22H2, 21H2...etc)

    Was this answer helpful?

    0 comments No comments