' cx='32' cy='32' r='32' /%3E%3Ctext x='50%25' y='55%25' dominant-baseline='middle' text-anchor='middle' fill='%23FFF' %3EA%3C/text%3E%3C/svg%3E)


A scheduled task triggers the command. Please do the following:
- Boot into Safe mode. https://support.microsoft.com/en-us/windows/windows-startup-settings-1af6ec8c-4d4a-4b23-adb7-e76eef0b847f
Open admin Command Prompt and run these commands:
- netsh.exe winhttp reset proxy
- bitsadmin /util /setieproxy localsystem NO_PROXY RESET
- rd /s /q C:\Windows\system32\DomainAuthHost
Post the output.
- Share your Farbar scan logs for analysis.
- Download Farbar Recovery Scan Tool 64-bit (FRST64.exe)
https://www.bleepingcomputer.com/download/farbar-recovery-scan-tool/
Note: If Microsoft Edge or Chrome mislabels the Farbar Scanner executable as PUA/malware, choose to keep it by tapping … in the bottom bar, choosing Keep, and then choosing Keep anyway in the dialog that appears.
See this screenshot: https://learn.microsoft.com/en-us/deployedge/media/microsoft-edge-security-download-interruptions/dowload-was-blocked.png. It's a safe tool used in most antimalware forums.
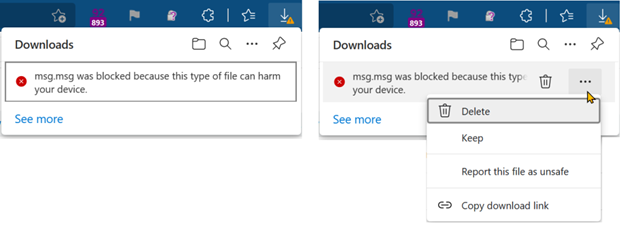
- If the OS language is not English, rename FRST64.exe to FRST64English.exe.
- Run the program. Don't check or uncheck any options. Click "Scan".
- Add the two logs, FRST.txt and Addition.txt, to a Zip archive, share them on OneDrive or GoFile.io and post the link here.
**************************************************************
Additional note:
The Trojan:PowerShell/DownInfo.BA threat detection was added to Defender on 6/10/2025 10:52 PM (in security intelligence version 1.429.460.0). That's the same day the latest cumulative update was released. This makes the users think the LCU caused this 'false-detection'. In reality, their systems were already infected, and the infection came to light after installing security intelligence update version 1.429.460.0 on June 10.
**************************************************************