Virus .udjvu

Anonymous
2018-12-23T10:14:35+00:00

Yesterday I was using my computer normally then suddenly a popup showed telling me that there was updates installing and I knew that it's not from Microsoft  as when I opened the source from task manger I found that it's not related to Microsoft updates so I click on end task then I tried to open Windows defender but it showed this message " page not available Your IT administrator as limited access to some areas of this app, and the item you tried to access is not available. Contact IT helpdesk for more information. Then I found that a program called windows powershell is installed by itself .. Then the screen blacked out showing only this message when I tried to open Task manger " Task manger has been disabled by your administrator" 

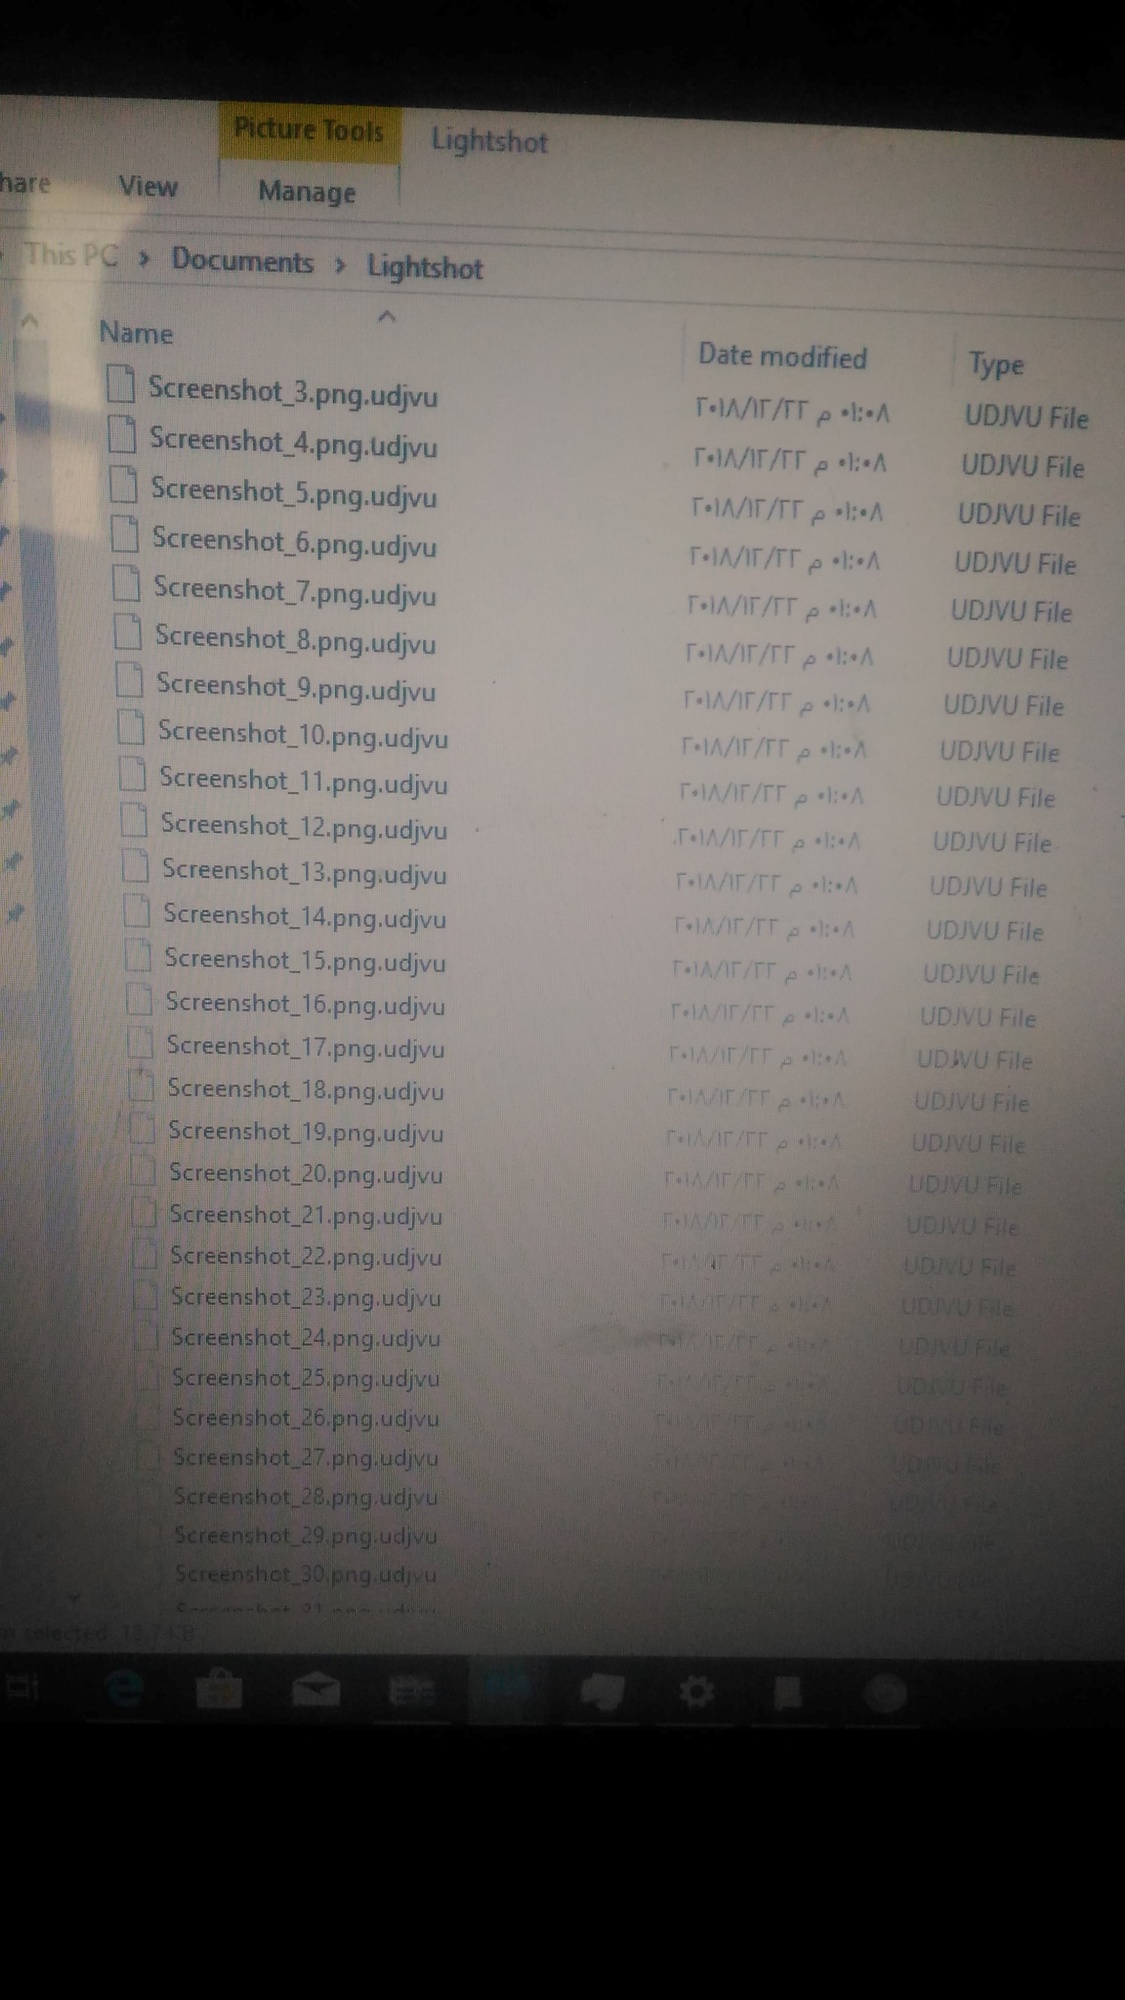
SO I tried to restart the my computer but couldn't open start...after managing to restart by pressing the  power button for awhile to restore windows from a restore points , there was three but all failed and also repair failed so click on reset my computer but keep my files ..when it finished I found all my files "pictures , programs , pdfs, doxc, " all of it ended with this extension

.udjvu

like in the picture attached 

So How can I get my files back and open them?

"when I tried to use snap tool I didn't find it"
Windows for home | Windows 10 | Security and privacy

Locked Question. This question was migrated from the Microsoft Support Community. You can vote on whether it's helpful, but you can't add comments or replies or follow the question.

0 comments No comments

52 answers

Sort by: Newest
  1. quietman7 MVP Alumni 19,830 Reputation points Volunteer Moderator
    2019-01-12T14:11:32+00:00

    Did you read the entire topic and my previous comments?

    Each victim's decrypter provided by the malware developer is unique to them and cannot be used with someone else's encrypted files. Sharing a decrypter provided by the cyber-criminals with another victim who paid the ransom will not work since the keys are different for each individual case.

    Was this answer helpful?

    0 comments No comments
  2. Deleted

    This answer has been deleted due to a violation of our Code of Conduct. The answer was manually reported or identified through automated detection before action was taken. Please refer to our Code of Conduct for more information.


    Comments have been turned off. Learn more

  3. quietman7 MVP Alumni 19,830 Reputation points Volunteer Moderator
    2019-01-10T13:01:13+00:00

    Although Michael Gillespie (aka Demonslay335) released a free decryption tool (STOPDecrypter) for victims of the .puma, .pumas and .pumax STOP Ransomware variants and Dr.Web is able to decrypt the .DATAWAIT and .INFOWAIT variants as noted here by Emmanuel_ADC-Soft, there is no known method at this time to decrypt files encrypted by most other STOP Ransomware variants (including the .djvu, .djvuu, .udjvu, .djvuq, .uudjvu, .djvus, .djvur, .djvut, .djvup variants) without paying the ransom and obtaining the private RSA keys from the criminals unless they are leaked or seized & released by authorities. Without the master private RSA key that can be used to decrypt your files, decryption is impossible. Ignore all Google searches that say otherwise.

    Was this answer helpful?

    0 comments No comments
  4. Anonymous
    2019-01-10T05:45:02+00:00

    while searching on web for a decryption tool, spyhunter is being recommended by many. Please advice if it works for UDJVU Encryption

    Thanks

    Was this answer helpful?

    0 comments No comments
  5. quietman7 MVP Alumni 19,830 Reputation points Volunteer Moderator
    2019-01-08T02:47:44+00:00

    Typically with ransomware, each victim's decrypter (decoder) provided by the malware developer is unique to them with their own private randomly generated RSA decryption key, password or personal ID which cannot be used with someone else's encrypted files. Sharing a decrypter, decryption key, password or personal ID provided by the cyber-criminals with another victim who paid the ransom will not work since the keys are different for each individual case. There are rare exceptions such as CryptoWall 3.0's decrypter where the criminals provided a unique KEY file, along with a standardized decrypt.exe file which decrypted based on that KEY file.

    Further, there is no guarantee that the decrypter provided by the cyber-criminals will work properly and in some cases using an  incorrect or faulty decrypter may cause additional damage or corruption of the already encrypted files.

    Was this answer helpful?

    0 comments No comments