Location is greyed out, i cannot remove internet explorer 11 addon after virus removal

Anonymous
2015-09-22T16:27:00+00:00

I am running Windows 10 64 bit

After removing a virus using windows defender and malwarebytes, I could no longer...

A. remove these internet explorer add ons, to wit:

  1. Ó¦Óñ¦Ò»¼ü°²×°²å¼þ npQQPhoneManagerExt.dll
  2. 电脑管家网页防火墙 TSWebMon64.dat

B. activate Location in Notification since it is always greyed out now

Windows for home | Windows 10 | Security and privacy

Locked Question. This question was migrated from the Microsoft Support Community. You can vote on whether it's helpful, but you can't add comments or replies or follow the question.

0 comments No comments

157 answers

Sort by: Oldest
  1. Anonymous
    2015-09-25T07:21:57+00:00

    BHOs are more complex than search providers such as Google. I don't have one installed to inspect. I've asked the moderator for an opinion on 4 free BHO removers. I think one of them should be tried.

    In the meantime...

    (1) Open Explorer to C:.

    (2) Type or paste "TSWebMon64.dat" into the search box.

    (3) Go back to C:, & type "npQQPhoneManagerExt.dll" into the search box.

    (4) Go back to C:, & type "Tencent" into the search box.

    Are any found? Then, Defender & Malwarebytes may have extracted the virus, but they left a lot of junk behind. Post pictures. Here is how to look in the registry...

    --- I cannot find any of the files.....

    The search gives me an empty match...

    Was this answer helpful?

    0 comments No comments
  2. Anonymous
    2015-09-25T07:35:45+00:00

    Excellent. Good news for all Defender & Malwarebytes users. What about the registry?

    Was this answer helpful?

    0 comments No comments
  3. Anonymous
    2015-09-25T08:06:53+00:00

    BHOs are more complex than search providers such as Google. I don't have one installed to inspect. I've asked the moderator for an opinion on 4 free BHO removers. I think one of them should be tried.

    In the meantime...

    (1) Open Explorer to C:.

    (2) Type or paste "TSWebMon64.dat" into the search box.

    (3) Go back to C:, & type "npQQPhoneManagerExt.dll" into the search box.

    (4) Go back to C:, & type "Tencent" into the search box.

    Are any found? Then, Defender & Malwarebytes may have extracted the virus, but they left a lot of junk behind. Post pictures. Here is how to look in the registry...

    (1) R-Clk START, & select "Run".

    (2) Type "RegEdit" into the box, & hit ENTER.

    If you are not at the top (where it says "Computer"),

    click into the left pane & press the "Home" button on the keyboard.

    You need to be at the top for the start of each search...

    (3) Click the "Edit" menu, & select "Find".

    (4) Type or paste a Class ID into the search box, and hit ENTER.

         F3 will find the next occurrence (but you may need to hold the "FN" key as well).

    (5) Do a search for the file associated with that Class ID & the folder "Tencent" as well.

    (6) Do the same for the other Class ID - or - perhaps its best to do one BHO at a time, if there are a lot of hits.

    Post pictures of the left & right panes. Don't delete anything yet. I'm really hoping one of those BHO removers will do all the work for us.

    Was this answer helpful?

    0 comments No comments
  4. Anonymous
    2015-09-25T09:50:05+00:00

    It is redundant to check the "Reply with quote" box (as that appears to be what you are doing). The post one replies to can be seen by clicking the "In reply to..." that appears in every response...

    (1) I want to see what you get with a search for...
    ...which came up in the R-pane of your first search. This is a complexity of BHOs, that they spread out a bit in the registry.

    (2) I'm not sure what your 2nd search was for. But, judging by what I see in my own registry for that key,...
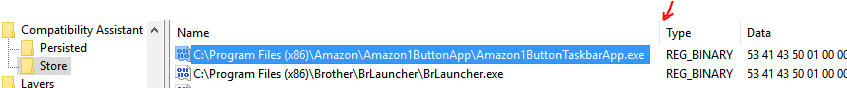
    ...it was one of the files. Had you double-clicked the separator line in the title bar between "Name" & "Type", the name area would have expanded to reveal it. But - no matter - this "Store" key can be ignored, I think. It is not actually part of the BHO.

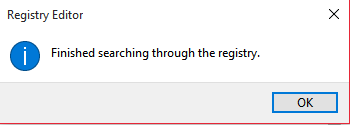
    (3) I see the 1st search result was for one Class ID & 3rd search result was for the other. But did you go back to the top of the registry to start the search for the other? And did you hit F3 to continue each search (find next) for more results? When the last result is reached, you get this...
    (4) I really don't like the looks of...
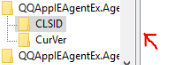
    ...in your 3rd result. You can grab those double lines with the cursor & drag to the right to reveal the full names. If we pursue this, I'd also want a search from the top of that name, "QQAppIEAgentEx.Age etc.".

    But I continue to await a report on those 4 BHO removers. If none arrives soon, I'll resume my own investigation for a trusty one. One of those needs be tried before we do any deleting of our own!

    Was this answer helpful?

    0 comments No comments
  5. Anonymous
    2015-09-26T15:46:12+00:00

    For the class ID {50F4150A-48B2-417A-BE4C-C83F580FB904}, the First Add-on, the search came up with 15 items....

    1.

    2.

    Was this answer helpful?

    0 comments No comments