Fixed with 27766 Workaround for “Your organization used App Control for Business to block this app” dialog in the Canary Channel

Anonymous
2024-12-16T16:39:34+00:00

After updating to Build 27764 in the Canary Channel, some Windows Insiders are reporting hitting the issue that previously impacted the Dev Channel where an “Your organization used App Control for Business to block this app” dialog is shown when attempting to use or install certain third-party apps on your PC due to an incorrect policy being enforced. The following steps should mitigate the issue:

  1. Open Command Prompt with administrator privileges.
  2. Type and hit enter: mountvol s: /s
  3. Type and hit enter: del S:\EFI\Microsoft\Boot\cipolicies\active{8E8A94F0-6EB9-42C7-A189-E018C8CF3D10}.cip
  4. Type and hit enter: del S:\EFI\Microsoft\Boot\cipolicies\active{36D62F7C-AB85-4F61-8724-744294F24023}.cip
  5. Type and hit enter: del S:\EFI\Microsoft\Boot\cipolicies\active{66D7D265-7EDD-47DD-86E4-F7C42CD55A8F}.cip
  6. Then reboot your PC.

If you are dual-booting between the Canary Channel and the Dev Channel or another version of Windows, you will need to do this workaround BEFORE booting to the other OS.

If the above steps do not work, you may need to disable Secure Boot first and follow these steps:

  1. Disable Secure Boot on your PC.
  2. You will be asked to enter your BitLocker recovery key.
  3. Log in to your PC and open Command Prompt with administrator privileges.
  4. Type and hit enter: mountvol s: /s
  5. Type and hit enter: del S:\EFI\Microsoft\Boot\cipolicies\active{8E8A94F0-6EB9-42C7-A189-E018C8CF3D10}.cip
  6. Type and hit enter: del S:\EFI\Microsoft\Boot\cipolicies\active{36D62F7C-AB85-4F61-8724-744294F24023}.cip
  7. Type and hit enter: del S:\EFI\Microsoft\Boot\cipolicies\active{66D7D265-7EDD-47DD-86E4-F7C42CD55A8F}.cip
  8. Reboot your PC once with Secure Boot still disabled.
  9. Then reboot again and enable Secure Boot.

In small cases, your PC may not boot into Windows. To get out of this state, you can follow these steps:

  1. Disable Secure Boot on your PC.
  2. Then get into Windows Recovery, choose advanced boot options and disable driver signature enforcement.
  3. Then do the above-mentioned workaround for deleting the policies after logging in.
  4. Alternatively, you can also delete the above-mentioned policies directly from the Windows Recovery console.
Windows Insider program | Windows Insider preview | Install, activate, and Windows update

Locked Question. This question was migrated from the Microsoft Support Community. You can vote on whether it's helpful, but you can't add comments or replies or follow the question.

0 comments No comments

91 answers

Sort by: Newest
  1. Anonymous
    2025-01-14T07:14:43+00:00

    I remove even all the accounts on the windows, I let only a local account -> same thing.

    I tried to check the intune thing from microsoft, when I try to rich to the Endpoints, i have a 403 or 401 unauthorized, I spoke with the admin, and he said that he did not set any policy for the organization.

    The update messed the windows really good.

    Was this answer helpful?

    0 comments No comments
  2. Anonymous
    2025-01-14T06:53:36+00:00

    Thank you for the reply.

    I think the partition for efi is S , but here I don't find the files that everybody talks.

    The workaround that I found but drive me crazy is altering the startup settings every time I start the letter, and disabling driver signature enforcement

    If I run mountvol G: /d , I get the system cannot find the file specified.
    Image

    On saturday I made a rollback ,because after the update I had problems with the Internet too, I was connected to the internet (wi-fi/enthernet/hotspot) and I did not got anything (I got something like access blocked ) , the internet worked just fine on other devices.

    After the rollback I was able to use the internet, and I saw that I did not had the G:\ partition, but yesterday after I tried almost everything I thought , if i will reset the windows maybe I will be able to get rid get rid of the policies thing, and "Your organzation used App Control for Business to block this app". But nothing happened after the reset.

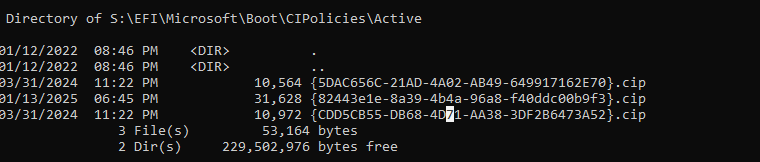
    From what you show above the bad CIPolicies files have already been deleted.

    Any problem you have seems to be unrelated to those files. 🤷‍♂️

    If you have a good system image backup taken before you had these problems, you could just restore a good system.

    Otherwise, you may try an update repair with the repair version. Good luck!

    Was this answer helpful?

    0 comments No comments
  3. Anonymous
    2025-01-14T06:39:42+00:00

    Thank you for the reply.

    I think the partition for efi is S , but here I don't find the files that everybody talks.

    The workaround that I found but drive me crazy is altering the startup settings every time I start the letter, and disabling driver signature enforcement

    If I run mountvol G: /d , I get the system cannot find the file specified.

    Image

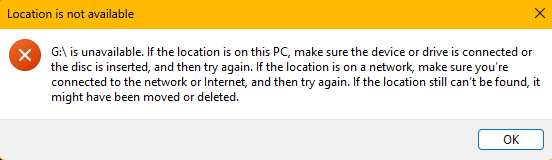
    I tried to create a folder in the G:\ to see what happens there , and I get this error.
    On saturday I made a rollback ,because after the update I had problems with the Internet too, I was connected to the internet (wi-fi/enthernet/hotspot) and I did not got anything (I got something like access blocked ) , the internet worked just fine on other devices.

    After the rollback I was able to use the internet, and I saw that I did not had the G:\ partition, but yesterday after I tried almost everything I thought , if i will reset the windows maybe I will be able to get rid get rid of the policies thing, and "Your organzation used App Control for Business to block this app". But nothing happened after the reset.

    Was this answer helpful?

    0 comments No comments
  4. Anonymous
    2025-01-13T20:13:25+00:00

    Hello,

    I tried to find the policies but i don't have the policies in S ,

    Coult not find S:\EFI\Microsoft\Boot\cipolicies\active{8E8A94F0-6EB9-42C7-A189-E018C8CF3D10}.cip , I even reset the windows, and i still get the error.

    I see that I got a G:\ partition, but I don't have anything there, and this partition weren't there, is out of nowhere this partition right now.

    Some users found that the EFI partition was mounted already with a different letter.

    In that case you should get an error when you try to "mountvol S: /s"

    Perhaps yours is mounted on G: instead of S: 🤷‍♂️

    If that is the case, you can remove G: and mountvol on S: again.

    mountvol G: /d

    mountvol S: /s

    then type the following to check the files in the directory and then delete the ones suggested. 😎

    S:

    S:>cd EFI\Microsoft/boot/cipolicies\active

    dir

    https://learn.microsoft.com/en-us/windows-server/administration/windows-commands/mountvol

    Was this answer helpful?

    0 comments No comments
  5. Anonymous
    2025-01-13T19:12:55+00:00

    Hello,

    I tried to find the policies but i don't have the policies in S ,

    Coult not find S:\EFI\Microsoft\Boot\cipolicies\active{8E8A94F0-6EB9-42C7-A189-E018C8CF3D10}.cip , I even reset the windows, and i still get the error.

    I see that I got a G:\ partition, but I don't have anything there, and this partition weren't there, is out of nowhere this partition right now.

    Was this answer helpful?

    0 comments No comments