' cx='32' cy='32' r='32' /%3E%3Ctext x='50%25' y='55%25' dominant-baseline='middle' text-anchor='middle' fill='%23FFF' %3EMR%3C/text%3E%3C/svg%3E)

' cx='32' cy='32' r='32' /%3E%3Ctext x='50%25' y='55%25' dominant-baseline='middle' text-anchor='middle' fill='%23FFF' %3EA%3C/text%3E%3C/svg%3E)
' cx='32' cy='32' r='32' /%3E%3Ctext x='50%25' y='55%25' dominant-baseline='middle' text-anchor='middle' fill='%23FFF' %3EG%3C/text%3E%3C/svg%3E)
' cx='32' cy='32' r='32' /%3E%3Ctext x='50%25' y='55%25' dominant-baseline='middle' text-anchor='middle' fill='%23FFF' %3EBE%3C/text%3E%3C/svg%3E)
' cx='32' cy='32' r='32' /%3E%3Ctext x='50%25' y='55%25' dominant-baseline='middle' text-anchor='middle' fill='%23FFF' %3EMN%3C/text%3E%3C/svg%3E)
' cx='32' cy='32' r='32' /%3E%3Ctext x='50%25' y='55%25' dominant-baseline='middle' text-anchor='middle' fill='%23FFF' %3EI%3C/text%3E%3C/svg%3E)
' cx='32' cy='32' r='32' /%3E%3Ctext x='50%25' y='55%25' dominant-baseline='middle' text-anchor='middle' fill='%23FFF' %3EGR%3C/text%3E%3C/svg%3E)
' cx='32' cy='32' r='32' /%3E%3Ctext x='50%25' y='55%25' dominant-baseline='middle' text-anchor='middle' fill='%23FFF' %3EJM%3C/text%3E%3C/svg%3E)
' cx='32' cy='32' r='32' /%3E%3Ctext x='50%25' y='55%25' dominant-baseline='middle' text-anchor='middle' fill='%23FFF' %3EF%3C/text%3E%3C/svg%3E)

I have engaged Microsoft Support on this. We checked a few things:
1) Double check that all antivirus exclusions are set up properly, as per Microsoft recommendations: https://learn.microsoft.com/en-us/azure/architecture/example-scenario/wvd/windows-virtual-desktop-fslogix (antivirus exclusions section).
2) Experiment with changing a few registry key values affecting the FsLogix profile operations, as per: https://learn.microsoft.com/en-us/fslogix/profile-container-configuration-reference.
3) Took procmon and etl traces in a working and non-working scenario, since this is occurring to some of the users. First analysis of procmon did not show any permissions violations, all CloseFile events by the FsLogix service (run with NT Authority\SYSTEM credentials) seems to be clean (SUCCESS). Now waiting on analysis of the procmon and etl logs from another round of testing by Microsoft Support.
4) Stop and disable the "Connected User Experiences and Telemetry" Windows service, as this has been seen to cause issues with profile release operations in Microsoft RDS/UPD environments. Nothing changed, issue persists.
5) Check FsLogix redirections.xml file configuration. This testing is in progress and more details are included in the following post: https://stefanos.cloud/blog/kb/how-to-resolve-error-group-policy-client-service-failed-the-logon-access-denied-in-citrix-and-fslogix-environments/.

' cx='32' cy='32' r='32' /%3E%3Ctext x='50%25' y='55%25' dominant-baseline='middle' text-anchor='middle' fill='%23FFF' %3EMG%3C/text%3E%3C/svg%3E)
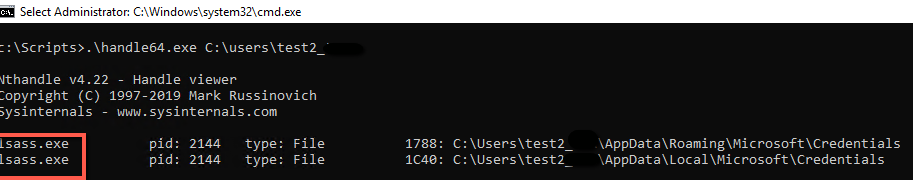
 released, see attached screenshot.
' cx='32' cy='32' r='32' /%3E%3Ctext x='50%25' y='55%25' dominant-baseline='middle' text-anchor='middle' fill='%23FFF' %3ED%3C/text%3E%3C/svg%3E)
