Main Issue:
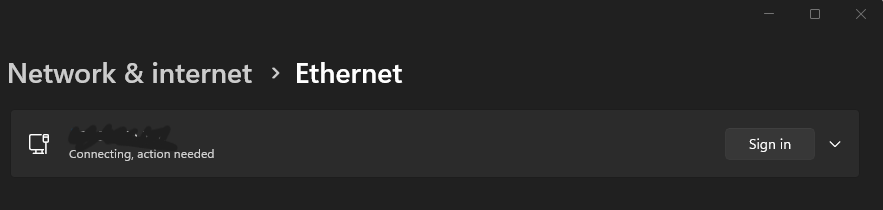
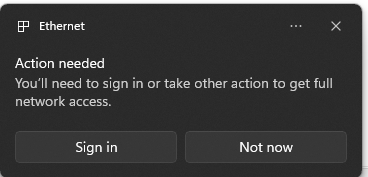
Using EAP-TEAP GPO (Windows Server 2022) for Windows 11 devices, clients are able to use the machine cert to auth with no issues. Once the user logs into windows, the user gets a notification that "Network Action needed'. That action basically requires you to navigate to settings > Network & Internet > Ethernet > Click the Sign on button. Once you do that, windows prompt for a pin (because it's using your external smart card user cert). Once the pin is good, the device is able to do all the stuff and things and is happily connected to the network using the machine/user cert. The big deal is that action of 'action needed' and requiring users to auth to the network instead of it just prompting for a pin. This happens with both wired and wireless. Pics will be attached of the prompt and where the sign in button is located.
However, when we did this with a windows 10 machine, the user logs into windows, and after a minute they just get a pin prompt, then they are able to connect to the network (using EAP-TEAP machine&user cert)
I can't figure out how to make this action prompt go away and just connect without having the user to do the whole settings, ethernet, click sign in. I just want a pin prompt and connect.
Main GPO Setting details:
Computer configuration > Policies > Windows Settings > Security Settings > Wired Network
Using IEEE 802.1x auth for network access
Netowrk Auth Method: 'EAP TEAP'
Auth mode: 'User or Computer auth'
Inner Method: Primary Auth
EAP-TLS (smartcard or other certificate)
Use my smart card
use simple cert selection (from PKI root ca)
certificate must contain Smart Card Logon
Validate ISE Server cert with our dc ca cert
Inner Method: Secondary Auth
EAP-TLS (smartcard or other certificate)
Use a cert on this compute
use simple cert selection
Cert must be issues by our dc02 cert (EKU all purpose and client auth)
Validate ISE Server cert with our dc ca cert
Advanced Settings:
Enforce advanced 802.1x settings
transmit per IEEE 802.1x
Enable Single Sign On for this network
Perform immediately before User logon
***There is also a wireless GPO and pretty much is the same as wired just has the BSSID and always connect to this network
Machine cert is issued from Active Directory We are using a physical smart card that has 4 certs, 1 is for user smart card login. does require a pin Login to windows/workstation requires to have a smart card, using that same cert i want to user for 802.1x eap-teap.
Workstation is a Windows 11 version 23H2 Domian is a windows server 2022, that's where the GPO was configured. I've seen things about credential guard, making sure the CA certs are selected, I've tried with and without the trusted server FQDN (with case matching). I saw something about win10 vs 10 eap-teap profile .xml sha hash, but to me that's with trusted the radius server and that's not an issue. Everything works, cert auto select works, just i have to sign in to the network each time through that prompt and going into settings, ethernet sign in. and for some reason any command with netsh does not run. could be some policy issue but i do see our computers complete eap-teap in ISE of course after i do the whole prompt sign in process.
also, the ISE cert and is from our local CA, it's selected and trusted. the smart card cert if from a different public CA, that's trusted on ISE. Again, it works, just getting that prompt
Thanks for your time, I'll try to keep update things i have done as well as any possible suggestions i receive.
' cx='32' cy='32' r='32' /%3E%3Ctext x='50%25' y='55%25' dominant-baseline='middle' text-anchor='middle' fill='%23FFF' %3ES%3C/text%3E%3C/svg%3E)

' cx='32' cy='32' r='32' /%3E%3Ctext x='50%25' y='55%25' dominant-baseline='middle' text-anchor='middle' fill='%23FFF' %3EPM%3C/text%3E%3C/svg%3E)
' cx='32' cy='32' r='32' /%3E%3Ctext x='50%25' y='55%25' dominant-baseline='middle' text-anchor='middle' fill='%23FFF' %3ESK%3C/text%3E%3C/svg%3E)
' cx='32' cy='32' r='32' /%3E%3Ctext x='50%25' y='55%25' dominant-baseline='middle' text-anchor='middle' fill='%23FFF' %3EAI%3C/text%3E%3C/svg%3E)
' cx='32' cy='32' r='32' /%3E%3Ctext x='50%25' y='55%25' dominant-baseline='middle' text-anchor='middle' fill='%23FFF' %3ECT%3C/text%3E%3C/svg%3E)